The ASP.NET Resource Kit is available:
"The ASP.NET Resource Kit is available for download free of charge from http://www.msdn.microsoft.com/asp.net/asprk. Developers can also order a copy of the Resource Kit on CD for a small shipping and handling fee.
The MSDN ASP.NET Migration Center and the ASP to ASP.NET and PHP to ASP.NET Migration Guides are located at http://www.msdn.microsoft.com/asp.net/using/migrating/."
http://www.msdn.microsoft.com/asp.net/asprk
Saturday, March 13, 2004


Friday, March 12, 2004
Advanced Placement Digital Library in Biology, Physics, and Chemistry:
"Advanced Placement (AP) teachers and students will find resources linked to the AP content outlines, published by the College Board, in biology, physics, and chemistry."
http://apdl.rice.edu/DesktopDefault.aspx
"Advanced Placement (AP) teachers and students will find resources linked to the AP content outlines, published by the College Board, in biology, physics, and chemistry."
http://apdl.rice.edu/DesktopDefault.aspx
Tuesday, March 09, 2004
Symantec Security Response - W32.Netsky@mm Removal Tool:
"Symantec Security Response has developed a removal tool to clean infections of the following Netsky variants.
W32.Netsky.B@mm
W32.Netsky.C@mm
W32.Netsky.D@mm
W32.Netsky.E@mm
W32.Netsky.K@mm"
http://securityresponse.symantec.com/avcenter/venc/data/w32.netsky@mm.removal.tool.html
"Symantec Security Response has developed a removal tool to clean infections of the following Netsky variants.
W32.Netsky.B@mm
W32.Netsky.C@mm
W32.Netsky.D@mm
W32.Netsky.E@mm
W32.Netsky.K@mm"
http://securityresponse.symantec.com/avcenter/venc/data/w32.netsky@mm.removal.tool.html
The Hidden Power of Photoshop CS: Chapter 2: Color Separations. Pt. 1. By Sybex - WebReference.com-:
"Photoshop provides many tools that seem to produce some magic behind the scenes. Channels, one of the most prominent of these tools, allow you to work directly with components of a color model, such as RGB or CMYK. But, as we saw in the previous chapter, channels can actually be simulated using some simple light theory. Understanding what the channels represent can help you make more intelligent color and correction decisions, and can very much change the way you work with images.… "
http://www.webreference.com/graphics/ps1/
"Photoshop provides many tools that seem to produce some magic behind the scenes. Channels, one of the most prominent of these tools, allow you to work directly with components of a color model, such as RGB or CMYK. But, as we saw in the previous chapter, channels can actually be simulated using some simple light theory. Understanding what the channels represent can help you make more intelligent color and correction decisions, and can very much change the way you work with images.… "
http://www.webreference.com/graphics/ps1/
Linux Privilege Escalation Hole Detected:
"For the second time in as many months, security researchers have uncovered a privilege escalation security flaw in the Linux kernel.…"
The flaw carries a "critical" rating and affects Linux versions 2.2 up to and including 2.2.25; it also impacts versions 2.4 up to and including 2.4.24 as well as versions 2.6 up to and including 2.6.2.
"Proper exploitation of this vulnerability leads to local privilege escalation giving an attacker full super-user privileges. The vulnerability may also lead to a denial-of-service attack on the available system memory," iSEC warned.
Linux distributor Gentoo confirmed its implementation of the open source operating system was susceptible to the flaw and strongly urged uses to upgrade to newer, more secure versions.
According to Gentoo, arbitrary code with normal non-superuser privileges may be able to exploit this vulnerability and may disrupt the operation of other parts of the kernel memory management subroutines.
Proper exploitation of this vulnerability may lead to local privilege escalation allowing for the execution of arbitrary code with kernel level root access," Gentoo warning, noting that proof-of-concept exploit code has been created and successfully tested.
The flaw was discovered in the memory subsystem which allows for shrinking, growing, and moving of chunks of memory along any of the allocated memory areas which the kernel possesses. iSEC Security Research found that the code doesn't check the return value of the memory function.…
http://www.internetnews.com/dev-news/article.php/3322911
"For the second time in as many months, security researchers have uncovered a privilege escalation security flaw in the Linux kernel.…"
The flaw carries a "critical" rating and affects Linux versions 2.2 up to and including 2.2.25; it also impacts versions 2.4 up to and including 2.4.24 as well as versions 2.6 up to and including 2.6.2.
"Proper exploitation of this vulnerability leads to local privilege escalation giving an attacker full super-user privileges. The vulnerability may also lead to a denial-of-service attack on the available system memory," iSEC warned.
Linux distributor Gentoo confirmed its implementation of the open source operating system was susceptible to the flaw and strongly urged uses to upgrade to newer, more secure versions.
According to Gentoo, arbitrary code with normal non-superuser privileges may be able to exploit this vulnerability and may disrupt the operation of other parts of the kernel memory management subroutines.
Proper exploitation of this vulnerability may lead to local privilege escalation allowing for the execution of arbitrary code with kernel level root access," Gentoo warning, noting that proof-of-concept exploit code has been created and successfully tested.
The flaw was discovered in the memory subsystem which allows for shrinking, growing, and moving of chunks of memory along any of the allocated memory areas which the kernel possesses. iSEC Security Research found that the code doesn't check the return value of the memory function.…
http://www.internetnews.com/dev-news/article.php/3322911
How to Use Command Line Shortcuts:
"How to Use Command Line Shortcuts"
http://www.microsoft.com/WindowsXP/expertzone/columns/ballew/commandline.asp
"How to Use Command Line Shortcuts"
http://www.microsoft.com/WindowsXP/expertzone/columns/ballew/commandline.asp
Windows XP Support Secrets:
"Windows XP Support Secrets"
http://www.microsoft.com/WindowsXP/expertzone/columns/bott/suppsec.asp
"Windows XP Support Secrets"
http://www.microsoft.com/WindowsXP/expertzone/columns/bott/suppsec.asp
Finding Help Online for New Users:
"Finding Help Online for New Users"
http://www.microsoft.com/windowsxp/expertzone/columns/ballew/02august19.asp
"Finding Help Online for New Users"
http://www.microsoft.com/windowsxp/expertzone/columns/ballew/02august19.asp
Worms Are For Suckers Page 2:
"BE VERY SKEPTICAL OF ANY ATTACHMENT IN E-MAIL. This doesn't mean that you shouldn't trust any attachment at all, but unless you know the sender and were expecting the file, you should scrutinize it and not open it unless you can determine that it's legitimate.
Keep your antivirus software and firewall up to date. They aren't perfect, but they help a lot.
If your mail client can block all executables, let it. Most worms, including NetSky, will be blocked just by this. If not, find some other way to do it. It's just not worth being able to mail executables around. Incidentally, both Outlook and Outlook Express have done this for years, and therefore their users have been immune to these worms. "
http://www.eweek.com/article2/0,1759,1543635,00.asp
"BE VERY SKEPTICAL OF ANY ATTACHMENT IN E-MAIL. This doesn't mean that you shouldn't trust any attachment at all, but unless you know the sender and were expecting the file, you should scrutinize it and not open it unless you can determine that it's legitimate.
Keep your antivirus software and firewall up to date. They aren't perfect, but they help a lot.
If your mail client can block all executables, let it. Most worms, including NetSky, will be blocked just by this. If not, find some other way to do it. It's just not worth being able to mail executables around. Incidentally, both Outlook and Outlook Express have done this for years, and therefore their users have been immune to these worms. "
http://www.eweek.com/article2/0,1759,1543635,00.asp
Worm Masquerades as MyDoom Patch:
"A new worm purporting to contain a patch to defend against MyDoom is attacking Windows machines throughout Europe and parts of North America.
Sober.D appeared Sunday and began spreading in Germany and the United Kingdom. The worm arrives in an e-mail message with a subject line of 'Microsoft Alert: Please Read!' and carries a sending address with a Microsoft domain. The domain extension on the messages are typically from Germany, Israel, Switzerland or Austria. "
The new worm comes a week after the largest, most concentrated onslaught of virus activity in recent memory, which included the appearances of 16 new viruses within about 10 days. Most of those new threats were variants of existing viruses, including MyDoom. The original version of Sober hit the Internet last October and never amounted to much.
Many of the samples of the new variant that antivirus vendors have seen so far have been written in German. The body of the infected message reads:
"New MyDoom Virus Variant Detected! A new variant of the W32.Mydoom (W32.Novarg) worm spread rapidly through the Internet. Anti-virus vendor Central Command claims that 1 in 45 e-mails contains the MyDoom virus. The worm also has a backdoor Trojan capability. By default, the Trojan component listens on port 13468. Protection: Please download this digitally signed attachment. This Update includes the functionality of previously released patches."
The message includes a file attachment that is either an executable or a Zip archive, according to Network Associates Inc.'s analysis of Sober.D. Once installed on a machine, the virus will display a phony error message indicating either that the fake patch has been installed or does not need to be installed on the PC.
Sober.D then scours the machine's hard drive for e-mail addresses and begins mailing itself out.…
http://www.eweek.com/article2/0,1759,1544482,00.asp?kc=EWNWS030804DTX1K0000599
"A new worm purporting to contain a patch to defend against MyDoom is attacking Windows machines throughout Europe and parts of North America.
Sober.D appeared Sunday and began spreading in Germany and the United Kingdom. The worm arrives in an e-mail message with a subject line of 'Microsoft Alert: Please Read!' and carries a sending address with a Microsoft domain. The domain extension on the messages are typically from Germany, Israel, Switzerland or Austria. "
The new worm comes a week after the largest, most concentrated onslaught of virus activity in recent memory, which included the appearances of 16 new viruses within about 10 days. Most of those new threats were variants of existing viruses, including MyDoom. The original version of Sober hit the Internet last October and never amounted to much.
Many of the samples of the new variant that antivirus vendors have seen so far have been written in German. The body of the infected message reads:
"New MyDoom Virus Variant Detected! A new variant of the W32.Mydoom (W32.Novarg) worm spread rapidly through the Internet. Anti-virus vendor Central Command claims that 1 in 45 e-mails contains the MyDoom virus. The worm also has a backdoor Trojan capability. By default, the Trojan component listens on port 13468. Protection: Please download this digitally signed attachment. This Update includes the functionality of previously released patches."
The message includes a file attachment that is either an executable or a Zip archive, according to Network Associates Inc.'s analysis of Sober.D. Once installed on a machine, the virus will display a phony error message indicating either that the fake patch has been installed or does not need to be installed on the PC.
Sober.D then scours the machine's hard drive for e-mail addresses and begins mailing itself out.…
http://www.eweek.com/article2/0,1759,1544482,00.asp?kc=EWNWS030804DTX1K0000599
Monday, March 08, 2004
mezzoblue revised image replacement:
"Plenty of new and interesting revisions to the original Fahrner Image Replacement technique have sprouted up recently. This is an attempt to consolidate them, so that perhaps we can decide on the official replacement.
Requirements: the replacement must solve the screen reader problem, and it must address the 'images off, css on' problem. It is also hoped that a solution will be found that reduces the need for empty elements. The successful technique must work in browsers back to 5.x, but as of the time of writing none of these appear to fail so browser support matrices will be spared.
The two most promising techniques, Phrak and Gilder/Levin are available on a reduced page for screenreader testing."
http://www.mezzoblue.com/tests/revised-image-replacement/
"Plenty of new and interesting revisions to the original Fahrner Image Replacement technique have sprouted up recently. This is an attempt to consolidate them, so that perhaps we can decide on the official replacement.
Requirements: the replacement must solve the screen reader problem, and it must address the 'images off, css on' problem. It is also hoped that a solution will be found that reduces the need for empty elements. The successful technique must work in browsers back to 5.x, but as of the time of writing none of these appear to fail so browser support matrices will be spared.
The two most promising techniques, Phrak and Gilder/Levin are available on a reduced page for screenreader testing."
http://www.mezzoblue.com/tests/revised-image-replacement/
ZDNet AnchorDesk: Virus 'gangs' to blame for recent epidemic:
"It's a busy time for computer viruses and worms. Over the last three weeks, we've seen nearly two dozen variations of Bagle, Netsky, and MyDoom circulate the Net. What gives? It looks like gang warfare is responsible, drive-by shootings on the information highway."
YOU HEARD ME right. "Gangs" of virus writers are currently trying to outdo one another and protect their turf. What they're fighting for is control of thousands of Trojan horses that create stealth peer-to-peer networks out of virus-infected computers worldwide. Such networks can be used to launch next-generation computer viruses or distributed denial-of-service attacks. They can also be sold to spammers who use them to anonymously send messages to our inboxes. Because of all their uses, virus writers consider these networks worth fighting for.
Unfortunately, you and I aren't just bystanders, we're the targets. And the only solution I can offer is what I've been saying for years: Update your antivirus software and don't open unsolicited e-mail messages. I wish there were a magic fix I could offer that would inoculate us all from these viruses, but, unfortunately, I can't. These infections aren't even very original. They use good old-fashioned social engineering, and not a software flaw, to spread.
There appear to be three distinct gangs: the MyDoomers, who are using source code from the MyDoom.b worm to set up stealth networks; the Bagles, who wrote their own unique viral code to establish the same sorts of networks; and the Netskys, who seem to have started the whole imbroglio by thwarting the plans laid down by MyDoom and Bagle.
THE FIGHT seems to have broken out on Feb. 18, when Netsky.b appeared on the Net and began removing traces of MyDoom and Bagle from infected computers. Netsky.b not only removed the viral code, but also the Trojan horse "back doors." These are the tunnels of communication that allow the MyDoom and Bagle gangs to communicate with infected systems and thus set up the valuable peer-to-peer networks. Needless to say, the authors of the Bagle and MyDoom variants took offense--as Netsky spread, their networks began to shrink in size and thus their ability to do harm online diminished.
One week later, on Feb. 25, the Netsky.c variant appeared a hidden message embedded in the code: "We are the skynet--you can't hide yourself---we kill malware...MyDoom.f is a thief of our idea!" (Such messages are known as "greetz.") A few days later, Bagle.J and MyDoom.G responded: "Hey, NetSky...Don't ruin our business, wanna start a war?" and "To NetSky's creator(s): imho, skynet is a decentralized peer-to-peer neural network. We have seen P2P in Slapper in Sinit only. They may be called skynets, but not your...app." (Slapper is a Linux worm that established its own P2P network starting in August 2002; Sinit is a common Trojan horse that also established its own P2P network, starting in October 2003.)
Greetz are not new; often they are directed at rival Internet gangs or antivirus researchers. In December of 2001, rival members of Israeli script kiddie gangs unwittingly released the Goner virus. In that case, the virus (which they called Pentagone) contained greetz with Internet nicknames of the authors: "Pentagone coded by: suid, tested by: ThE_SkuLL and Isatanl." Originally, the authors named in the greetz denied their involvement; shortly thereafter, however, they took credit for the virus when the news media started saying the code was cut and pasted from elsewhere. A short time later, the Israeli youths were arrested and sentenced to 2.5 years in jail.…
http://reviews-zdnet.com.com/AnchorDesk/4520-7297_16-5124832.html?tag=adss
"It's a busy time for computer viruses and worms. Over the last three weeks, we've seen nearly two dozen variations of Bagle, Netsky, and MyDoom circulate the Net. What gives? It looks like gang warfare is responsible, drive-by shootings on the information highway."
YOU HEARD ME right. "Gangs" of virus writers are currently trying to outdo one another and protect their turf. What they're fighting for is control of thousands of Trojan horses that create stealth peer-to-peer networks out of virus-infected computers worldwide. Such networks can be used to launch next-generation computer viruses or distributed denial-of-service attacks. They can also be sold to spammers who use them to anonymously send messages to our inboxes. Because of all their uses, virus writers consider these networks worth fighting for.
Unfortunately, you and I aren't just bystanders, we're the targets. And the only solution I can offer is what I've been saying for years: Update your antivirus software and don't open unsolicited e-mail messages. I wish there were a magic fix I could offer that would inoculate us all from these viruses, but, unfortunately, I can't. These infections aren't even very original. They use good old-fashioned social engineering, and not a software flaw, to spread.
There appear to be three distinct gangs: the MyDoomers, who are using source code from the MyDoom.b worm to set up stealth networks; the Bagles, who wrote their own unique viral code to establish the same sorts of networks; and the Netskys, who seem to have started the whole imbroglio by thwarting the plans laid down by MyDoom and Bagle.
THE FIGHT seems to have broken out on Feb. 18, when Netsky.b appeared on the Net and began removing traces of MyDoom and Bagle from infected computers. Netsky.b not only removed the viral code, but also the Trojan horse "back doors." These are the tunnels of communication that allow the MyDoom and Bagle gangs to communicate with infected systems and thus set up the valuable peer-to-peer networks. Needless to say, the authors of the Bagle and MyDoom variants took offense--as Netsky spread, their networks began to shrink in size and thus their ability to do harm online diminished.
One week later, on Feb. 25, the Netsky.c variant appeared a hidden message embedded in the code: "We are the skynet--you can't hide yourself---we kill malware...MyDoom.f is a thief of our idea!" (Such messages are known as "greetz.") A few days later, Bagle.J and MyDoom.G responded: "Hey, NetSky...Don't ruin our business, wanna start a war?" and "To NetSky's creator(s): imho, skynet is a decentralized peer-to-peer neural network. We have seen P2P in Slapper in Sinit only. They may be called skynets, but not your...app." (Slapper is a Linux worm that established its own P2P network starting in August 2002; Sinit is a common Trojan horse that also established its own P2P network, starting in October 2003.)
Greetz are not new; often they are directed at rival Internet gangs or antivirus researchers. In December of 2001, rival members of Israeli script kiddie gangs unwittingly released the Goner virus. In that case, the virus (which they called Pentagone) contained greetz with Internet nicknames of the authors: "Pentagone coded by: suid, tested by: ThE_SkuLL and Isatanl." Originally, the authors named in the greetz denied their involvement; shortly thereafter, however, they took credit for the virus when the news media started saying the code was cut and pasted from elsewhere. A short time later, the Israeli youths were arrested and sentenced to 2.5 years in jail.…
http://reviews-zdnet.com.com/AnchorDesk/4520-7297_16-5124832.html?tag=adss
Saturday, March 06, 2004
Alias Reduces Educational Pricing on Alias SketchBook Pro: "
Alias, a Silicon Graphics Inc. company, announced special educational pricing for Alias SketchBook Pro, the sketching, annotation and presentation software for Tablet PCs and Wacom tablets. Following a restructuring of its education program in July 2003 to provide affordable and accessible Maya and StudioTools learning packages, Alias is now expanding the program to include reduced pricing on Alias SketchBook Pro for both students and faculty.
Alias SketchBook Pro provides the latest in accurate digital sketching technology for industries such as industrial and product design, architecture, computer graphics, animation, game development and fashion design. Students looking to break into these industries can benefit from combining tools like Alias SketchBook Pro and a Tablet PC or Wacom tablet to hone their skills and develop a portfolio of exceptional creative work.…"
www.alias.com
www.journeyed.com
http://www.emedialive.com/Newsletters/EMediaXtra.aspx?NewsletterID=140#4
Alias, a Silicon Graphics Inc. company, announced special educational pricing for Alias SketchBook Pro, the sketching, annotation and presentation software for Tablet PCs and Wacom tablets. Following a restructuring of its education program in July 2003 to provide affordable and accessible Maya and StudioTools learning packages, Alias is now expanding the program to include reduced pricing on Alias SketchBook Pro for both students and faculty.
Alias SketchBook Pro provides the latest in accurate digital sketching technology for industries such as industrial and product design, architecture, computer graphics, animation, game development and fashion design. Students looking to break into these industries can benefit from combining tools like Alias SketchBook Pro and a Tablet PC or Wacom tablet to hone their skills and develop a portfolio of exceptional creative work.…"
www.alias.com
www.journeyed.com
http://www.emedialive.com/Newsletters/EMediaXtra.aspx?NewsletterID=140#4
Paid Inclusion Under Fire at Search Engine Shindig:
"The debate over the fairness and relevancy of paid search spilled onto the stage at the Jupitermedia's Search Engine Strategies 2004 conference here on Wednesday.
On one side: Google Inc., which objects to any commingling of paid search with its Web index. On the other: Yahoo Inc., which embraced this week a program for letting Web sites pay to be included in its recently launched Web index. "
And in the middle: Ask Jeeves Inc., which has dropped one paid program, where Web sites could provide XML feeds into its index, while maintaining another for paying to submit sites for crawling.
The varying positions demonstrate the evolving field of Web search. The battle to deliver the most relevant results, and to make money, has intensified now that Yahoo has switched from Google's search results to its own technology and as Microsoft Corp. builds its own technology.
The latest shift was Ask Jeeves discontinuation of its Index Express program for direct XML feeds into its Teoma search engine index. Paul Gardi, Ask Jeeves senior vice president of operations and planning, said the company was not denouncing the practice of paid inclusion but dropped that form because it didn't return relevant results for users.…
Ask Jeeves, of Emeryville, Calif., is continuing its Site Submit program, where sites pay to guarantee that their pages get crawled, Gardi said.
But Google and Yahoo, in a far-reaching panel discussion here on the future of search, did stake out clear opinions on whether Web sites should be able to pay to ensure their pages are indexed.
Google will continue to ban any paid inclusion into its Web search index, said Craig Silverstein, Google's director of technology, which drew applause from the audience. The Mountain View, Calif., company follows a strict division between its advertising business for sponsored search links and its ranking of regular results, he said.…
http://www.eweek.com/article2/0,1759,1541921,00.asp
http://www.eweek.com/article2/0,1759,1542441,00.asp?kc=EWNWS030404DTX1K0000599
"The debate over the fairness and relevancy of paid search spilled onto the stage at the Jupitermedia's Search Engine Strategies 2004 conference here on Wednesday.
On one side: Google Inc., which objects to any commingling of paid search with its Web index. On the other: Yahoo Inc., which embraced this week a program for letting Web sites pay to be included in its recently launched Web index. "
And in the middle: Ask Jeeves Inc., which has dropped one paid program, where Web sites could provide XML feeds into its index, while maintaining another for paying to submit sites for crawling.
The varying positions demonstrate the evolving field of Web search. The battle to deliver the most relevant results, and to make money, has intensified now that Yahoo has switched from Google's search results to its own technology and as Microsoft Corp. builds its own technology.
The latest shift was Ask Jeeves discontinuation of its Index Express program for direct XML feeds into its Teoma search engine index. Paul Gardi, Ask Jeeves senior vice president of operations and planning, said the company was not denouncing the practice of paid inclusion but dropped that form because it didn't return relevant results for users.…
Ask Jeeves, of Emeryville, Calif., is continuing its Site Submit program, where sites pay to guarantee that their pages get crawled, Gardi said.
But Google and Yahoo, in a far-reaching panel discussion here on the future of search, did stake out clear opinions on whether Web sites should be able to pay to ensure their pages are indexed.
Google will continue to ban any paid inclusion into its Web search index, said Craig Silverstein, Google's director of technology, which drew applause from the audience. The Mountain View, Calif., company follows a strict division between its advertising business for sponsored search links and its ranking of regular results, he said.…
http://www.eweek.com/article2/0,1759,1541921,00.asp
http://www.eweek.com/article2/0,1759,1542441,00.asp?kc=EWNWS030404DTX1K0000599
Wednesday, March 03, 2004
Microsoft Sparks Web Services for eBay:
"Specifically, developers may use Microsoft Office Excel 2003 spreadsheet and Microsoft Office FrontPage Web design applications to write services where eBay users could automate pricing and bid changes as needed. "
Participants in the eBay Developers Program can use XML application programming interfaces (APIs) with FrontPage 2003 to design Web sites that display custom information on items for sale on eBay. FrontPage 2003 includes Web design and maintenance tools and customized data views for listing multiple auction items.
With Excel 2003, users can: use XML to integrate with the eBay API to customize list views, graphs and charts; catalog bulk items online or offline; and submit item listings. The software allows eBay buyers and sellers to create a transaction record, analyze buying or selling history, and use automated uploading processes to submit listings.
To try the solution, users can download sample code with the eBay listing management capabilities within Microsoft Office from the eBay Developer site here.
http://developer.ebay.com/DevProgram/sign_in.asp?URL=/devzone/docs/samplecode.asp
http://www.internetnews.com/ec-news/article.php/3319641
"Specifically, developers may use Microsoft Office Excel 2003 spreadsheet and Microsoft Office FrontPage Web design applications to write services where eBay users could automate pricing and bid changes as needed. "
Participants in the eBay Developers Program can use XML application programming interfaces (APIs) with FrontPage 2003 to design Web sites that display custom information on items for sale on eBay. FrontPage 2003 includes Web design and maintenance tools and customized data views for listing multiple auction items.
With Excel 2003, users can: use XML to integrate with the eBay API to customize list views, graphs and charts; catalog bulk items online or offline; and submit item listings. The software allows eBay buyers and sellers to create a transaction record, analyze buying or selling history, and use automated uploading processes to submit listings.
To try the solution, users can download sample code with the eBay listing management capabilities within Microsoft Office from the eBay Developer site here.
http://developer.ebay.com/DevProgram/sign_in.asp?URL=/devzone/docs/samplecode.asp
http://www.internetnews.com/ec-news/article.php/3319641
Saturday, February 28, 2004
Netsky causing billions in damages - News - ZDNet:
"Despite requiring the computer user to actively run an attachment, Netsky.C seems to be spreading fast, with anti-virus vendor Central Command claiming it had discovered 1,500 infections of the virus within 40 minutes of its discovery. Like Netsky.B the latest virus uses its own SMTP engine to e-mail itself to addresses found on the computer, and copies itself into any folder it finds whose name includes 'shar'. "
UK security company mi2g estimated the economic damage done by Netsky.B worldwide to be at least US$3.12 billion. This was calculated "on the basis of helpdesk support costs, overtime payments, contingency outsourcing, loss of business, bandwidth clogging, productivity erosion, management time reallocation, cost of recovery, and software upgrades".…
http://zdnet.com.com/2100-1105_2-5165642.html
"Despite requiring the computer user to actively run an attachment, Netsky.C seems to be spreading fast, with anti-virus vendor Central Command claiming it had discovered 1,500 infections of the virus within 40 minutes of its discovery. Like Netsky.B the latest virus uses its own SMTP engine to e-mail itself to addresses found on the computer, and copies itself into any folder it finds whose name includes 'shar'. "
UK security company mi2g estimated the economic damage done by Netsky.B worldwide to be at least US$3.12 billion. This was calculated "on the basis of helpdesk support costs, overtime payments, contingency outsourcing, loss of business, bandwidth clogging, productivity erosion, management time reallocation, cost of recovery, and software upgrades".…
http://zdnet.com.com/2100-1105_2-5165642.html
Thursday, February 26, 2004
Caller ID for E-Mail Technical Specification:
"'Caller ID for E-Mail: The Next Step to Deterring Spam' is the Microsoft draft specification to address the widespread problem of domain spoofing. Domain spoofing refers specifically to the use of someone else's domain name when sending a message, and is part of the larger spoofing problem, the practice of forging the sender's address on e-mail messages.
Caller ID for e-mail would verify that each e-mail message originates from the Internet domain it claims to come from. Eliminating domain spoofing will help legitimate senders protect their domain names and reputations, and help recipients more effectively identify and filter junk e-mail."
http://www.microsoft.com/mscorp/twc/privacy/spam_callerid.mspx
"'Caller ID for E-Mail: The Next Step to Deterring Spam' is the Microsoft draft specification to address the widespread problem of domain spoofing. Domain spoofing refers specifically to the use of someone else's domain name when sending a message, and is part of the larger spoofing problem, the practice of forging the sender's address on e-mail messages.
Caller ID for e-mail would verify that each e-mail message originates from the Internet domain it claims to come from. Eliminating domain spoofing will help legitimate senders protect their domain names and reputations, and help recipients more effectively identify and filter junk e-mail."
http://www.microsoft.com/mscorp/twc/privacy/spam_callerid.mspx
Fresh Worms Attack E-Mail, Internet Explorer, User Data:
"A series of new worms spread on the Internet on Wednesday, spreading through conventional e-mail methods. The new versions have escalated their attacks and destructiveness. "
On the prowl is MyDoom.F worm, which began action on Monday. It is the latest version one of most successful worms on record; earlier MyDoom variants in January launched a series of distributed denial of service attacks (DDoS) against Microsoft Corp. and The SCO Group. The new version retains its predecessors' capability to perform a DDoS attack.
"What is interesting about these latest worm trends is that they are very politically motivated. More than your curious teenage hacker at work; these attacks are stemming from groups seeking to make a statement on some of today's most controversial technology issues," said Scott Chasin, chief technology officer of MX Logic Inc., in a statement.
Beyond its DDoS target, MyDoom.F is also more destructive. A PC Magazine analysis of MyDoom.F, said the worm attempts to delete files on the system based on a probabilistic formula, adding an element of destructiveness rarely seen in such worms.
The worm also attempts to spread to file sharing users. For all these reasons, antivirus vendors are giving it a higher threat ranking than usual.
The latest threat is NetSky.C, which arrived on Wednesday. The worm is a variant of NetSky.B, which spread rapidly earlier this month, according to security vendors. It is also called Moodown.C.
According to F-Secure Corp.'s analysis of the worm, the new version is compressed with a different program. It also behaves differently in several ways than its predecessor, such as searching far more files for e-mail addresses that it can use to spread itself.
The worm arrives in a ZIP file attachment to an e-mail message. The file inside the ZIP will have two file extensions, the first for an innocuous file type such as .RTF and the second for an executable file type, such as .SCR.…
http://www.eweek.com/article2/0,4149,1538954,00.asp?kc=EWNWS022604DTX1K0000599
"A series of new worms spread on the Internet on Wednesday, spreading through conventional e-mail methods. The new versions have escalated their attacks and destructiveness. "
On the prowl is MyDoom.F worm, which began action on Monday. It is the latest version one of most successful worms on record; earlier MyDoom variants in January launched a series of distributed denial of service attacks (DDoS) against Microsoft Corp. and The SCO Group. The new version retains its predecessors' capability to perform a DDoS attack.
"What is interesting about these latest worm trends is that they are very politically motivated. More than your curious teenage hacker at work; these attacks are stemming from groups seeking to make a statement on some of today's most controversial technology issues," said Scott Chasin, chief technology officer of MX Logic Inc., in a statement.
Beyond its DDoS target, MyDoom.F is also more destructive. A PC Magazine analysis of MyDoom.F, said the worm attempts to delete files on the system based on a probabilistic formula, adding an element of destructiveness rarely seen in such worms.
The worm also attempts to spread to file sharing users. For all these reasons, antivirus vendors are giving it a higher threat ranking than usual.
The latest threat is NetSky.C, which arrived on Wednesday. The worm is a variant of NetSky.B, which spread rapidly earlier this month, according to security vendors. It is also called Moodown.C.
According to F-Secure Corp.'s analysis of the worm, the new version is compressed with a different program. It also behaves differently in several ways than its predecessor, such as searching far more files for e-mail addresses that it can use to spread itself.
The worm arrives in a ZIP file attachment to an e-mail message. The file inside the ZIP will have two file extensions, the first for an innocuous file type such as .RTF and the second for an executable file type, such as .SCR.…
http://www.eweek.com/article2/0,4149,1538954,00.asp?kc=EWNWS022604DTX1K0000599
Security Guru Unmoved by Gates' RSA Remarks:
"Schneier's Gates comments followed some anecdotes about how everyone can help solve the security problems facing all enterprises. 'Get involved,' he said. 'That's how we make changes. Otherwise security is something done to us.'
Most security systems affect multiple parties, he explained, but usually only one person makes the decision about how security is implemented. 'At this point it's a negotiation. The players with most power are the ones who get to decide what the final answer is,' Schneier said. 'The best way to effect security is to gain power in negotiations. The best way is to change the environment in which security decisions are being made. Change the agenda of the players. Change the outcome.'
Every person has to make security work for himself, he said. 'The goal of security systems is the most security for the least amount of trade-offs. The way to do that is to make the party who is best able to mitigate the risk responsible for the risk,' he said, saying that computer software companies at this point do not share in the risks of software security or insecurity. "
Schneier said one of the best and simplest "security systems" he's seen is the local convenience store or fast food restaurant that displays a sign at the cash register that says, "Purchase free if you don't get a receipt." The system is not designed as a customer service, as it may appear, he said. Rather, it's a means of co-opting the customer into keeping an eye on the store employee who may be suspected of skimming from the cash register. Nevertheless, the customer will be watching if he knows he could get something for free.
"Good security systems are in line with their capabilities," he said. "The store manager is hiring you, aligning your interests with your capabilities. Very cheap security system. For the money it's really good. That's what we should strive for in security systems. The goal is to make them as effective as possible and work with the natural tendencies of people already there."
http://www.eweek.com/print_article/0,3048,a=120200,00.asp
"Schneier's Gates comments followed some anecdotes about how everyone can help solve the security problems facing all enterprises. 'Get involved,' he said. 'That's how we make changes. Otherwise security is something done to us.'
Most security systems affect multiple parties, he explained, but usually only one person makes the decision about how security is implemented. 'At this point it's a negotiation. The players with most power are the ones who get to decide what the final answer is,' Schneier said. 'The best way to effect security is to gain power in negotiations. The best way is to change the environment in which security decisions are being made. Change the agenda of the players. Change the outcome.'
Every person has to make security work for himself, he said. 'The goal of security systems is the most security for the least amount of trade-offs. The way to do that is to make the party who is best able to mitigate the risk responsible for the risk,' he said, saying that computer software companies at this point do not share in the risks of software security or insecurity. "
Schneier said one of the best and simplest "security systems" he's seen is the local convenience store or fast food restaurant that displays a sign at the cash register that says, "Purchase free if you don't get a receipt." The system is not designed as a customer service, as it may appear, he said. Rather, it's a means of co-opting the customer into keeping an eye on the store employee who may be suspected of skimming from the cash register. Nevertheless, the customer will be watching if he knows he could get something for free.
"Good security systems are in line with their capabilities," he said. "The store manager is hiring you, aligning your interests with your capabilities. Very cheap security system. For the money it's really good. That's what we should strive for in security systems. The goal is to make them as effective as possible and work with the natural tendencies of people already there."
http://www.eweek.com/print_article/0,3048,a=120200,00.asp
News: Special Reports:
"RSA Conference: New lines of defense
The security companies and experts gathering at the RSA Conference 2004 in San Francisco are showing off smarter ways to ward off attacks. The problem is that hackers are becoming more sophisticated, too. At best, it's hoped that damage can be kept to a minimum."
http://zdnet.com.com/2251-1110-5163906.html
"RSA Conference: New lines of defense
The security companies and experts gathering at the RSA Conference 2004 in San Francisco are showing off smarter ways to ward off attacks. The problem is that hackers are becoming more sophisticated, too. At best, it's hoped that damage can be kept to a minimum."
http://zdnet.com.com/2251-1110-5163906.html
Wednesday, February 25, 2004
Service-Oriented Architecture: Chapter 13: Thirty best practices for integrating Web services. Pt. 1. - WebReference.com -:
"Service-Oriented Architecture: Chapter 13: Thirty best practices for integrating Web services, Pt. 1.
'This chapter is from the book 'Service-Oriented Architecture: A Field Guide to Integrating XML and Web Services' by Thomas Erl. (ISBN 0131428985)."
http://www.webreference.com/programming/soa/index.html
"Service-Oriented Architecture: Chapter 13: Thirty best practices for integrating Web services, Pt. 1.
'This chapter is from the book 'Service-Oriented Architecture: A Field Guide to Integrating XML and Web Services' by Thomas Erl. (ISBN 0131428985)."
http://www.webreference.com/programming/soa/index.html
Tuesday, February 24, 2004
Download details: Office 2003/XP Add-in: Remove Hidden Data:
"With this add-in you can permanently remove hidden data and collaboration data, such as change tracking and comments, from Microsoft Word, Microsoft Excel, and Microsoft PowerPoint files."
Thanks to WinXPnews at http://www.winxpnews.com
http://www.microsoft.com/downloads/details.aspx?FamilyID=144e54ed-d43e-42ca-bc7b-5446d34e5360&displaylang=en
"With this add-in you can permanently remove hidden data and collaboration data, such as change tracking and comments, from Microsoft Word, Microsoft Excel, and Microsoft PowerPoint files."
Thanks to WinXPnews at http://www.winxpnews.com
http://www.microsoft.com/downloads/details.aspx?FamilyID=144e54ed-d43e-42ca-bc7b-5446d34e5360&displaylang=en
Monday, February 23, 2004
Order the Windows Security Update CD:
"Order the Windows Security Update CD
Updated Date: February 23, 2004
The Windows Security Update CD will be shipped to you free of charge. This CD includes Microsoft critical updates released through October 2003 and information to help you protect your PC. In addition, you will also receive a free antivirus and firewall trial software CD.
This CD is only available for Windows XP, Windows Me, Windows 2000, Windows 98, and Windows 98 Second Edition (SE).
Please allow 2-4 weeks for delivery."
http://www.microsoft.com/security/protect/cd/order.asp
"Order the Windows Security Update CD
Updated Date: February 23, 2004
The Windows Security Update CD will be shipped to you free of charge. This CD includes Microsoft critical updates released through October 2003 and information to help you protect your PC. In addition, you will also receive a free antivirus and firewall trial software CD.
This CD is only available for Windows XP, Windows Me, Windows 2000, Windows 98, and Windows 98 Second Edition (SE).
Please allow 2-4 weeks for delivery."
http://www.microsoft.com/security/protect/cd/order.asp
Friday, February 20, 2004
Serious Linux Security Holes Uncovered and Patched:
"The Polish security non-profit organization iSEC Security Research on Wednesday released an advisory describing two 'critical security vulnerabilities' in Linux 2.4 and 2.6's 'kernel-memory-management code inside the 'mremap(2)' system call.… "
http://www.eweek.com/article2/0,4149,1530875,00.asp
"The Polish security non-profit organization iSEC Security Research on Wednesday released an advisory describing two 'critical security vulnerabilities' in Linux 2.4 and 2.6's 'kernel-memory-management code inside the 'mremap(2)' system call.… "
http://www.eweek.com/article2/0,4149,1530875,00.asp
Protect Your PC:
"* Exclusive offer for Microsoft customers. Free 12-month software subscription to CA's eTrust EZ Armor-LE Antivirus and Firewall security suite. Valid for new users only. Limit 1 per household. Not to be combined with any other offer. Customers may elect to upgrade to eTrust EZ Armor with enhanced firewall functionality. Annual subscriptions can be renewed after first year at current renewal rate. Free software offer expires 2/1/05. **IDC 2003. "
eTrust EZ Armor Security Suite from Computer Associates, the world's #1 supplier of Internet security software** combines award-winning Antivirus with industrial-strength Firewall protection. Built specifically for today's Internet-intensive computer user, eTrust EZ Armor leverages the core technology CA has developed for the world's most demanding users including over 99% of the Fortune 500.
EZ to install and a snap to use, eTrust EZ Armor provides automatic virus updates, advanced email attachment protection, EZ to use firewall settings, activity control to stop website monitoring, ad blocking and cookie control features for a more enjoyable Internet experience.
http://www.my-etrust.com/microsoft/
"* Exclusive offer for Microsoft customers. Free 12-month software subscription to CA's eTrust EZ Armor-LE Antivirus and Firewall security suite. Valid for new users only. Limit 1 per household. Not to be combined with any other offer. Customers may elect to upgrade to eTrust EZ Armor with enhanced firewall functionality. Annual subscriptions can be renewed after first year at current renewal rate. Free software offer expires 2/1/05. **IDC 2003. "
eTrust EZ Armor Security Suite from Computer Associates, the world's #1 supplier of Internet security software** combines award-winning Antivirus with industrial-strength Firewall protection. Built specifically for today's Internet-intensive computer user, eTrust EZ Armor leverages the core technology CA has developed for the world's most demanding users including over 99% of the Fortune 500.
EZ to install and a snap to use, eTrust EZ Armor provides automatic virus updates, advanced email attachment protection, EZ to use firewall settings, activity control to stop website monitoring, ad blocking and cookie control features for a more enjoyable Internet experience.
http://www.my-etrust.com/microsoft/
ZoneAlarm Bug Bares System to E-Mail Attack:
"Security vendor Zone Labs has disclosed that several versions of its personal-firewall products are vulnerable to a buffer-overflow attack that could compromise the system.
ZoneAlarm, ZoneAlarm Plus and ZoneAlarm Pro 4.0.0 versions; ZoneAlarm Pro 4.5.0; as well as Zone Labs Integrity Client 4.0.0 are vulnerable, the company said. Versions earlier than 4.0.0 are not. ZoneAlarm users are advised to upgrade to Version 4.5.538.001. (See the Zone Labs advisory for more details and how to obtain the upgrades.…"
http://download.zonelabs.com/bin/free/securityAlert/8.html
http://www.eweek.com/article2/0,4149,1531324,00.asp?kc=EWNWS022004DTX1K0000599
"Security vendor Zone Labs has disclosed that several versions of its personal-firewall products are vulnerable to a buffer-overflow attack that could compromise the system.
ZoneAlarm, ZoneAlarm Plus and ZoneAlarm Pro 4.0.0 versions; ZoneAlarm Pro 4.5.0; as well as Zone Labs Integrity Client 4.0.0 are vulnerable, the company said. Versions earlier than 4.0.0 are not. ZoneAlarm users are advised to upgrade to Version 4.5.538.001. (See the Zone Labs advisory for more details and how to obtain the upgrades.…"
http://download.zonelabs.com/bin/free/securityAlert/8.html
http://www.eweek.com/article2/0,4149,1531324,00.asp?kc=EWNWS022004DTX1K0000599
NetSky.B Worm Gains More Traction:
"A new mass-mailing worm, called NetSky.B, is spreading rapidly after beginning to make the rounds of e-mail inboxes on Tuesday.
NetSky.B is a variant of the NetSky.A worm identified earlier in the week, but is posing a greater risk of spreading and infecting machines, security vendors warned Wednesday. Symantec Corp. rated NetSky.B a Category 4 threat, its second-highest level, while Network Associates Inc. and F-Secure Corp. rated it as a medium threat.… "
Network Associates in its security alert (http://www.eweek.com/article2/0,4149,1530599,00.asp?kc=EWNWS022004DTX1K0000599) reports that NetSky.B attempts to deactivate the MyDoom.A and MyDoom.B viruses, which earlier this month overloaded e-mail inboxes worldwide and included payloads to trigger DoS (denial-of-service) attacks against the Web sites of the SCO Group Inc. and Microsoft Corp.
NetSky.B affects systems running Microsoft Windows 95 and higher.…
http://www.eweek.com/article2/0,4149,1530599,00.asp?kc=EWNWS022004DTX1K0000599
"A new mass-mailing worm, called NetSky.B, is spreading rapidly after beginning to make the rounds of e-mail inboxes on Tuesday.
NetSky.B is a variant of the NetSky.A worm identified earlier in the week, but is posing a greater risk of spreading and infecting machines, security vendors warned Wednesday. Symantec Corp. rated NetSky.B a Category 4 threat, its second-highest level, while Network Associates Inc. and F-Secure Corp. rated it as a medium threat.… "
Network Associates in its security alert (http://www.eweek.com/article2/0,4149,1530599,00.asp?kc=EWNWS022004DTX1K0000599) reports that NetSky.B attempts to deactivate the MyDoom.A and MyDoom.B viruses, which earlier this month overloaded e-mail inboxes worldwide and included payloads to trigger DoS (denial-of-service) attacks against the Web sites of the SCO Group Inc. and Microsoft Corp.
NetSky.B affects systems running Microsoft Windows 95 and higher.…
http://www.eweek.com/article2/0,4149,1530599,00.asp?kc=EWNWS022004DTX1K0000599
Wednesday, February 18, 2004
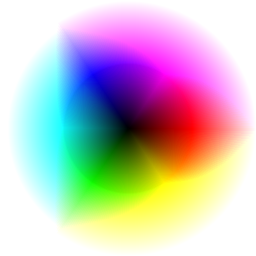
4096 Color Wheel:
"Hover over the wheel to view colors.
Click to choose a web-smart color.
Reload to clear."
Once, long ago, monitors could display only a restricted number of colors without dithering or other color discrepancies. The traditional solution to this problem was to use a restricted color palette known as the Netscape 216 colors, browser-safe colors or the web-safe colors. In hexadecimal form, the web-safe colors are composed of three pairs of identical hexadecimal digits selected from 00, 33, 66, 99, cc, and ff; for example, #000000 is black, and #ffffff is white.
Time passed, as it so frequently does, and new hardware supported thousands or millions of colors. People grew tired of the old 216 colors. They wanted more earth tones, more variety. The web-smart colors are those 4096 colors composed of any three pairs of identical hexadeximal digits (0-9 and a-f), such as #dd1188.
The unsafe colors are the full set of 16,777,216 hexadecimal colors, featuring any color between #000000 and #ffffff, such as #5a832d.
The current location of the 4096 Color Wheel is http://jemimap.ficml.org/style/color/wheel.html. The current version is 1.4. The Color Wheel is free for any use. To save it, download the html page and the image.
http://www.ficml.org/jemimap/style/color/colorwheel.png
http://www.ficml.org/jemimap/style/color/wheel.html
"Hover over the wheel to view colors.
Click to choose a web-smart color.
Reload to clear."
Once, long ago, monitors could display only a restricted number of colors without dithering or other color discrepancies. The traditional solution to this problem was to use a restricted color palette known as the Netscape 216 colors, browser-safe colors or the web-safe colors. In hexadecimal form, the web-safe colors are composed of three pairs of identical hexadecimal digits selected from 00, 33, 66, 99, cc, and ff; for example, #000000 is black, and #ffffff is white.
Time passed, as it so frequently does, and new hardware supported thousands or millions of colors. People grew tired of the old 216 colors. They wanted more earth tones, more variety. The web-smart colors are those 4096 colors composed of any three pairs of identical hexadeximal digits (0-9 and a-f), such as #dd1188.
The unsafe colors are the full set of 16,777,216 hexadecimal colors, featuring any color between #000000 and #ffffff, such as #5a832d.
The current location of the 4096 Color Wheel is http://jemimap.ficml.org/style/color/wheel.html. The current version is 1.4. The Color Wheel is free for any use. To save it, download the html page and the image.
http://www.ficml.org/jemimap/style/color/colorwheel.png
http://www.ficml.org/jemimap/style/color/wheel.html
Security Alert: Bagle.B Worm Growing Fast:
"While the last Bagle virus scare turned out to be more hole than actual 'bagel,' this new variant is showing some real substance and is spreading at a rate that has some virus watchers upping Bagle.B-mm's threat level.
W32/Bagle.B-mm, also known as W32/Tanx.A, and Beagle.B, is a mass mailing worm that is spreading at outbreak proportions. Discovered, early Tuesday morning, MessageLabs has recorded over 75,000 copies of the virus detected from their customer base by 5 pm, with a peak infection ratio of 1 virus in 16 emails. The virus was classified as a medium threat by most antivirus vendors. Like its predecessor, Bagle.A, it is more performance degrading than destructive, though it sets up a Trojan to listen at a backdoor port, and uses its own SMTP engine to send copies to email addresses it finds on a victims system.
Bagle.B infected e-mails arrive with spoofed 'From' addresses, often people you know.…"
The virus normally runs the Windows sound recorder (sndrec32.exe) when it executes, though according to an analysis by Norman (http://www.norman.com/virus_info/w32_bagle_b_mm.shtml) Antivirus, "this will not happen if the worm starts as result of an update process or if it is started from the System directory." Sound recorder is just an indicator of infection, and put in to confuse the victim, and is not used further ( figure 2 ). However, the virus does open and listen at port 8866 to receive downloads or commands from the virus author. According to Symantec's analysis (http://www.sarc.com/avcenter/venc/data/w32.beagle.b@mm.html) of Bagle.B, the virus "Sends HTTP GET requests every 10,000 seconds to the following Web sites on TCP port 80:
www.strato.de/1.php
www.strato.de/2.php
www.47df.de/wbboard/1.php
www.intern.games-ring.de/2.php
Symantec also notes: "The GET request includes the port number that the infected computer is listening on, and the ID number that is saved in the 'gid' key in the Windows registry. Also, by connecting to the web server, the IP address will be sent." To propagate, Bagle.B harvests e-mail addresses from text based files and the Windows address book on the victim's PC. The virus creates e-mail messages with copies of itself as randomly named attachments, and sends using its own SMTP engine. Bagle.B will not send to email addresses containing the following:
.r1u
@hotmail.com
@msn.com
@microsoft
@avp
http://www.pcmag.com/print_article/0,3048,a=119435,00.asp
"While the last Bagle virus scare turned out to be more hole than actual 'bagel,' this new variant is showing some real substance and is spreading at a rate that has some virus watchers upping Bagle.B-mm's threat level.
W32/Bagle.B-mm, also known as W32/Tanx.A, and Beagle.B, is a mass mailing worm that is spreading at outbreak proportions. Discovered, early Tuesday morning, MessageLabs has recorded over 75,000 copies of the virus detected from their customer base by 5 pm, with a peak infection ratio of 1 virus in 16 emails. The virus was classified as a medium threat by most antivirus vendors. Like its predecessor, Bagle.A, it is more performance degrading than destructive, though it sets up a Trojan to listen at a backdoor port, and uses its own SMTP engine to send copies to email addresses it finds on a victims system.
Bagle.B infected e-mails arrive with spoofed 'From' addresses, often people you know.…"
The virus normally runs the Windows sound recorder (sndrec32.exe) when it executes, though according to an analysis by Norman (http://www.norman.com/virus_info/w32_bagle_b_mm.shtml) Antivirus, "this will not happen if the worm starts as result of an update process or if it is started from the System directory." Sound recorder is just an indicator of infection, and put in to confuse the victim, and is not used further ( figure 2 ). However, the virus does open and listen at port 8866 to receive downloads or commands from the virus author. According to Symantec's analysis (http://www.sarc.com/avcenter/venc/data/w32.beagle.b@mm.html) of Bagle.B, the virus "Sends HTTP GET requests every 10,000 seconds to the following Web sites on TCP port 80:
www.strato.de/1.php
www.strato.de/2.php
www.47df.de/wbboard/1.php
www.intern.games-ring.de/2.php
Symantec also notes: "The GET request includes the port number that the infected computer is listening on, and the ID number that is saved in the 'gid' key in the Windows registry. Also, by connecting to the web server, the IP address will be sent." To propagate, Bagle.B harvests e-mail addresses from text based files and the Windows address book on the victim's PC. The virus creates e-mail messages with copies of itself as randomly named attachments, and sends using its own SMTP engine. Bagle.B will not send to email addresses containing the following:
.r1u
@hotmail.com
@msn.com
@microsoft
@avp
http://www.pcmag.com/print_article/0,3048,a=119435,00.asp
VoIP: It's not so easy to listen in - News - ZDNet:
"Jeff Pulver, founder of Free World Dialup, said Friday that if law enforcement officials asked him to wiretap one of his subscribers' Internet phone calls he would need a 'few months science project' to see if it could be done.
Meanwhile, Niklas Zennstrom, founder of Skype, also a free Internet phone service, said that even if his company could tackle the arduous task of pulling a Skype call from the Internet, police would 'only hear gibberish' because the data bits are encrypted."
The two providers are prime examples of a problem the Federal Communications Commission now faces after voting Thursday to investigate whether Internet phone providers should rewire their networks to government specifications to provide police with guaranteed access for wiretaps.
While many voice over Internet Protocol (VoIP) providers are more than willing to hand over whatever information they can about subscribers, they can't reliably, if at all, get what police really want: the content of the calls they make. Difficulties lie in gathering the millions of bits of information that represent a voice call as well as the fact that there is no standardized way for distinguishing voice calls from the terabits of other data on the Internet.
The issue affects a broad range of VoIP providers, including FWD and Skype, and commercial services such as Vonage and 8x8 that offer calls to traditional phone lines. Many of these commercial services say a sizable percentage of their calls never touch the traditional phone network and, as a result, cannot be tapped.…
http://zdnet.com.com/2100-1103_2-5159159.html
"Jeff Pulver, founder of Free World Dialup, said Friday that if law enforcement officials asked him to wiretap one of his subscribers' Internet phone calls he would need a 'few months science project' to see if it could be done.
Meanwhile, Niklas Zennstrom, founder of Skype, also a free Internet phone service, said that even if his company could tackle the arduous task of pulling a Skype call from the Internet, police would 'only hear gibberish' because the data bits are encrypted."
The two providers are prime examples of a problem the Federal Communications Commission now faces after voting Thursday to investigate whether Internet phone providers should rewire their networks to government specifications to provide police with guaranteed access for wiretaps.
While many voice over Internet Protocol (VoIP) providers are more than willing to hand over whatever information they can about subscribers, they can't reliably, if at all, get what police really want: the content of the calls they make. Difficulties lie in gathering the millions of bits of information that represent a voice call as well as the fact that there is no standardized way for distinguishing voice calls from the terabits of other data on the Internet.
The issue affects a broad range of VoIP providers, including FWD and Skype, and commercial services such as Vonage and 8x8 that offer calls to traditional phone lines. Many of these commercial services say a sizable percentage of their calls never touch the traditional phone network and, as a result, cannot be tapped.…
http://zdnet.com.com/2100-1103_2-5159159.html
Tuesday, February 17, 2004
Download details: Mydoom (A, B) and Doomjuice (A, B) Worm Removal Tool (KB836528):
"This tool will help to remove the Mydoom.A, Mydoom.B, Doomjuice.A (aka "MyDoom.C"), and Doomjuice.B worms from infected systems. Once the tool has run—after the End-User License Agreement (EULA) is accepted—it automatically checks for infection and removes any of the targeted worms that are found. If a machine is infected with the Mydoom.B worm, the tool will also provide the user with the default version of the hosts file and set the "read-only" attribute for that file. This action will allow the user to visit previously-blocked Microsoft and antivirus websites."
After running, the tool displays a message describing the outcome of the detection and removal process. The tool can be safely deleted after it has run. Also, the tool creates a log file named doomcln.log in the %WINDIR%\debug folder.
This tool will not:
Detect or remove any viruses or worms other than Mydoom.A, Mydoom.B, Doomjuice.A, and Doomjuice.B
Detect or remove future variants of Mydoom or Doomjuice
Prevent the machine from being re-infected with Mydoom if, for example, an infected e-mail attachment is re-executed
Detect or remove malware that exists on a system as a result of the backdoor component created by Mydoom.A or Mydoom.B (besides Doomjuice.A and Doomjuice.B).
Delete any e-mail that contains Mydoom.A or Mydoom.B
Run on any version of Windows NT 4.0
The user must be an administrator to run this tool.…
http://www.microsoft.com/downloads/details.aspx?FamilyID=c14bfbe4-3d50-464d-a26c-9c287f8a08c5&displaylang=en
"This tool will help to remove the Mydoom.A, Mydoom.B, Doomjuice.A (aka "MyDoom.C"), and Doomjuice.B worms from infected systems. Once the tool has run—after the End-User License Agreement (EULA) is accepted—it automatically checks for infection and removes any of the targeted worms that are found. If a machine is infected with the Mydoom.B worm, the tool will also provide the user with the default version of the hosts file and set the "read-only" attribute for that file. This action will allow the user to visit previously-blocked Microsoft and antivirus websites."
After running, the tool displays a message describing the outcome of the detection and removal process. The tool can be safely deleted after it has run. Also, the tool creates a log file named doomcln.log in the %WINDIR%\debug folder.
This tool will not:
Detect or remove any viruses or worms other than Mydoom.A, Mydoom.B, Doomjuice.A, and Doomjuice.B
Detect or remove future variants of Mydoom or Doomjuice
Prevent the machine from being re-infected with Mydoom if, for example, an infected e-mail attachment is re-executed
Detect or remove malware that exists on a system as a result of the backdoor component created by Mydoom.A or Mydoom.B (besides Doomjuice.A and Doomjuice.B).
Delete any e-mail that contains Mydoom.A or Mydoom.B
Run on any version of Windows NT 4.0
The user must be an administrator to run this tool.…
http://www.microsoft.com/downloads/details.aspx?FamilyID=c14bfbe4-3d50-464d-a26c-9c287f8a08c5&displaylang=en
Chicago Tribune | Spammers Exploit High-Speed Connections:
"Next time you're looking for a culprit for all that junk mail flooding your inbox, have a glance in the mirror. Spammers are increasingly exploiting home computers with high-speed Internet connections into which they've cleverly burrowed.
E-mail security companies estimate that between one-third and two-thirds of unwanted messages are relayed unwittingly by PC owners who set up software incorrectly or fail to secure their machines.… "
Hundreds of thousands of computers worldwide have been infected by SoBig and other viruses that are programmed to spawn gateways, known technically as proxies, to relay spam. Though Lawrence had antivirus software, he hadn't kept it updated.
It's ironic to the president of the security Web site myNetWatchman.com, Lawrence Baldwin, that those afflicted by spam are also often its couriers.…
Any Internet-connected computer could be running a proxy spam relay, but most of the malicious programs are written specifically for PCs that run Windows.
In the past, some spammers had sought out and exploited Internet-connected computers with misconfigured networking software. The latest and growing threat is code purposely written to create spam relay proxies as it is spread by malicious viruses.
"It's just going to get worse," said Ken Schneider, chief technology officer at spam-filtering company Brightmail Inc. "Traditionally, virus writers were driven more by reputation and trying to impress each other. Now there's an economic motive."
Just last week, a proxy program called Mitglieder began installing itself on computers infected by last month's Mydoom outbreak, said Mikko Hypponen, manager of antivirus research at F-Secure Corp. in Finland. He said such programs can also sneak in if computer owners fail to install patches to fix known Windows flaws.
The shift in spamming methods even prompted the Federal Trade Commission to issue a consumer alert last month. The advisory encouraged consumers to use antivirus and firewall programs and to check "sent mail" folders for suspicious messages.
Others say home users should also keep their Windows operating systems up to date by visiting http://windowsupdate.microsoft.com.
"If your computer has been taken over by a spammer, you could face serious problems," the FTC advisory wrote. "Your Internet Service Provider (ISP) may prevent you from sending any e-mail at all until the virus is treated, and treatment could be a complicated, time-consuming process.…"
http://www.chicagotribune.com/technology/sns-ap-spam-zombies,1,2703344.story?coll=chi-technology-hed
"Next time you're looking for a culprit for all that junk mail flooding your inbox, have a glance in the mirror. Spammers are increasingly exploiting home computers with high-speed Internet connections into which they've cleverly burrowed.
E-mail security companies estimate that between one-third and two-thirds of unwanted messages are relayed unwittingly by PC owners who set up software incorrectly or fail to secure their machines.… "
Hundreds of thousands of computers worldwide have been infected by SoBig and other viruses that are programmed to spawn gateways, known technically as proxies, to relay spam. Though Lawrence had antivirus software, he hadn't kept it updated.
It's ironic to the president of the security Web site myNetWatchman.com, Lawrence Baldwin, that those afflicted by spam are also often its couriers.…
Any Internet-connected computer could be running a proxy spam relay, but most of the malicious programs are written specifically for PCs that run Windows.
In the past, some spammers had sought out and exploited Internet-connected computers with misconfigured networking software. The latest and growing threat is code purposely written to create spam relay proxies as it is spread by malicious viruses.
"It's just going to get worse," said Ken Schneider, chief technology officer at spam-filtering company Brightmail Inc. "Traditionally, virus writers were driven more by reputation and trying to impress each other. Now there's an economic motive."
Just last week, a proxy program called Mitglieder began installing itself on computers infected by last month's Mydoom outbreak, said Mikko Hypponen, manager of antivirus research at F-Secure Corp. in Finland. He said such programs can also sneak in if computer owners fail to install patches to fix known Windows flaws.
The shift in spamming methods even prompted the Federal Trade Commission to issue a consumer alert last month. The advisory encouraged consumers to use antivirus and firewall programs and to check "sent mail" folders for suspicious messages.
Others say home users should also keep their Windows operating systems up to date by visiting http://windowsupdate.microsoft.com.
"If your computer has been taken over by a spammer, you could face serious problems," the FTC advisory wrote. "Your Internet Service Provider (ISP) may prevent you from sending any e-mail at all until the virus is treated, and treatment could be a complicated, time-consuming process.…"
http://www.chicagotribune.com/technology/sns-ap-spam-zombies,1,2703344.story?coll=chi-technology-hed
Friday, February 13, 2004
Accessible Web Typography - an introduction for web designers:
"A book by Jim Byrne
The author is available for accessible web design development and consultancy work: jim@scotconnect.com
The HTML version of the book is free:"
http://www.scotconnect.com/webtypography/
"A book by Jim Byrne
The author is available for accessible web design development and consultancy work: jim@scotconnect.com
The HTML version of the book is free:"
http://www.scotconnect.com/webtypography/
The Windows Patch—What You Need to Know :
"On Tuesday February 10th, Microsoft released three new security updates to patch new vulnerabilities, one of which is catching a lot of attention. Security Update MS04-007 is rated as critical because it has the potential to leave a user of Windows NT, 2000, XP or 2003 Server open to an attack that could result in remote code execution. The vulnerability has no workarounds, and is being very strongly recommended by Microsoft and security organizations. However, at this time, Microsoft says there are no reported incidents using the vulnerability, but is recommending the patch as a preemptive strike against attack.…"
http://www.pcmag.com/article2/0,4149,1525075,00.asp
"On Tuesday February 10th, Microsoft released three new security updates to patch new vulnerabilities, one of which is catching a lot of attention. Security Update MS04-007 is rated as critical because it has the potential to leave a user of Windows NT, 2000, XP or 2003 Server open to an attack that could result in remote code execution. The vulnerability has no workarounds, and is being very strongly recommended by Microsoft and security organizations. However, at this time, Microsoft says there are no reported incidents using the vulnerability, but is recommending the patch as a preemptive strike against attack.…"
http://www.pcmag.com/article2/0,4149,1525075,00.asp
Microsoft TechNet:
"Microsoft Security Bulletin MS04-007
ASN.1 Vulnerability Could Allow Code Execution (828028)"
Impact of vulnerability: Remote Code Execution
Maximum Severity Rating: Critical
Security Update Replacement: None
Caveats: Windows NT 4.0 (Workstation, Server, and Terminal Server Edition) does not install the affected file by default. This file is installed as part of the MS03-041 Windows NT 4.0 security update and other possible non-security-related hotfixes. If the Windows NT 4.0 security update for MS03-041 is not installed, this may not be a required update. To verify if the affected file is installed, search for the file named Msasn1.dll. If this file is present, this security update is required. Windows Update, Software Update Services, and the Microsoft Security Baseline Analyzer will also correctly detect if this update is required.…
http://www.microsoft.com/technet/treeview/?url=/technet/security/bulletin/MS04-007.asp
"Microsoft Security Bulletin MS04-007
ASN.1 Vulnerability Could Allow Code Execution (828028)"
Impact of vulnerability: Remote Code Execution
Maximum Severity Rating: Critical
Security Update Replacement: None
Caveats: Windows NT 4.0 (Workstation, Server, and Terminal Server Edition) does not install the affected file by default. This file is installed as part of the MS03-041 Windows NT 4.0 security update and other possible non-security-related hotfixes. If the Windows NT 4.0 security update for MS03-041 is not installed, this may not be a required update. To verify if the affected file is installed, search for the file named Msasn1.dll. If this file is present, this security update is required. Windows Update, Software Update Services, and the Microsoft Security Baseline Analyzer will also correctly detect if this update is required.…
http://www.microsoft.com/technet/treeview/?url=/technet/security/bulletin/MS04-007.asp
MyDoom author may be covering tracks - News - ZDNet:
"A worm that started spreading on Sunday places the source code for the original MyDoom virus on victims' hard drives, an action equivalent to planting evidence, antivirus experts said Tuesday.
The worm, Doomjuice, spreads to computers that have already been infected by either the original MyDoom virus or the MyDoom.B variant, and among other actions, places several copies of the source code for MyDoom.A on a victim's computer.
The author may be using the tactic to create a crowd of PC users in which to hide, or the author could be spreading the code in hopes that other virus writers will create variations on MyDoom, said Graham Cluley, senior technology consultant for antivirus company Sophos. "
Doomjuice is one of two opportunistic programs--the other dubbed Deadhat--that started spreading this week. Both viruses infect computers that have already succumbed to either of the two MyDoom viruses. Doomjuice also attempts to direct any re-infected PCs to attack Microsoft's Web site.
Doomjuice's possession of the source code for the original MyDoom virus suggests that the creator of the worm is also the writer of the original virus. A word in both MyDoom viruses--the name "andy"--has already suggested to some researchers that the original MyDoom and the MyDoom.B variant were created by the same person or group.
Other antivirus researchers agree that the latest hostile program could be intended to confuse investigations into who created the viruses.…
http://zdnet.com.com/2100-1104_2-5156836.html
"A worm that started spreading on Sunday places the source code for the original MyDoom virus on victims' hard drives, an action equivalent to planting evidence, antivirus experts said Tuesday.
The worm, Doomjuice, spreads to computers that have already been infected by either the original MyDoom virus or the MyDoom.B variant, and among other actions, places several copies of the source code for MyDoom.A on a victim's computer.
The author may be using the tactic to create a crowd of PC users in which to hide, or the author could be spreading the code in hopes that other virus writers will create variations on MyDoom, said Graham Cluley, senior technology consultant for antivirus company Sophos. "
Doomjuice is one of two opportunistic programs--the other dubbed Deadhat--that started spreading this week. Both viruses infect computers that have already succumbed to either of the two MyDoom viruses. Doomjuice also attempts to direct any re-infected PCs to attack Microsoft's Web site.
Doomjuice's possession of the source code for the original MyDoom virus suggests that the creator of the worm is also the writer of the original virus. A word in both MyDoom viruses--the name "andy"--has already suggested to some researchers that the original MyDoom and the MyDoom.B variant were created by the same person or group.
Other antivirus researchers agree that the latest hostile program could be intended to confuse investigations into who created the viruses.…
http://zdnet.com.com/2100-1104_2-5156836.html
Study: Spammers turning blind eye to the law - News - ZDNet:
"Only 3 percent of bulk commercial e-mail includes a valid U.S. postal mail address and a valid link to opt out of future messages, according to data released on Tuesday by MX Logic, a maker of mail-filtering software. Those requirements are part of the Can-Spam Act, short for Controlling the Assault of Non-Solicited Pornography and Marketing, the nation's first federal spam law.
What's more, the amount of spam has continued to grow since the law went into effect at the beginning of the year. As much as 60 percent of the e-mail sent in January was spam, up from 58 percent in December, according to San Francisco-based Brightmail, one of the largest spam-filtering companies.…"
http://zdnet.com.com/2100-1104_2-5156629.html?tag=adnews
"Only 3 percent of bulk commercial e-mail includes a valid U.S. postal mail address and a valid link to opt out of future messages, according to data released on Tuesday by MX Logic, a maker of mail-filtering software. Those requirements are part of the Can-Spam Act, short for Controlling the Assault of Non-Solicited Pornography and Marketing, the nation's first federal spam law.
What's more, the amount of spam has continued to grow since the law went into effect at the beginning of the year. As much as 60 percent of the e-mail sent in January was spam, up from 58 percent in December, according to San Francisco-based Brightmail, one of the largest spam-filtering companies.…"
http://zdnet.com.com/2100-1104_2-5156629.html?tag=adnews
Microsoft Warns Software Users of 'Critical' Flaw:
"The company called the software flaw a "critical" vulnerability, its highest rating. It is the second major security flaw announced this month by Microsoft, which recently began issuing regularly scheduled security patches for its software. "We urge all of our customers to apply this update," said Stephen Toulouse, a security program manager with Microsoft's security response center.
The flaw, one of three announced yesterday by Microsoft, affects a fundamental building block of network operating systems known as Abstract Syntax Notation One, and helps govern how machines communicate with one another and how they establish secure communications. Microsoft's version of that protocol is flawed, and could be used to gain control of the target machine. The company said there was no evidence that any attacks based on the flaw had occurred.… "
For now, Mr. Cooper said, computer users are probably safe because the flaw "is not exactly a simple one" to take advantage of, and no attack that would exploit the flaw had appeared on the hacker sites where such code is freely circulated. But once such an attack method is created, he said he expected to see a malicious program that could circulate via e-mail messaging and which would have as profound an effect on computer networks as the widespread "Blaster" worm of last year.…
http://www.nytimes.com/2004/02/11/technology/11worm.html
"The company called the software flaw a "critical" vulnerability, its highest rating. It is the second major security flaw announced this month by Microsoft, which recently began issuing regularly scheduled security patches for its software. "We urge all of our customers to apply this update," said Stephen Toulouse, a security program manager with Microsoft's security response center.
The flaw, one of three announced yesterday by Microsoft, affects a fundamental building block of network operating systems known as Abstract Syntax Notation One, and helps govern how machines communicate with one another and how they establish secure communications. Microsoft's version of that protocol is flawed, and could be used to gain control of the target machine. The company said there was no evidence that any attacks based on the flaw had occurred.… "
For now, Mr. Cooper said, computer users are probably safe because the flaw "is not exactly a simple one" to take advantage of, and no attack that would exploit the flaw had appeared on the hacker sites where such code is freely circulated. But once such an attack method is created, he said he expected to see a malicious program that could circulate via e-mail messaging and which would have as profound an effect on computer networks as the widespread "Blaster" worm of last year.…
http://www.nytimes.com/2004/02/11/technology/11worm.html
Wednesday, February 11, 2004
MyDoom.C Slams Into Microsoft.com:
"UPDATED: A stripped-down version of the MyDoom worm, a k a Doomjuice, on Monday spread through network backdoor and attacked Microsoft's Web site.
A new version of the MyDoom worm appears to be circulating on the Internet and may be responsible for some disruptions to Microsoft Corp.'s Web site Sunday night and Monday morning, researchers said.
When it's executed, the new variant, called MyDoom.C, or Doomjuice, begins scanning for machines listening on TCP port 3127. When it finds available PCs, it copies itself to the new machine's Windows directory under the file name 'intrenat.exe' and also creates a file named 'sync-src-1.00.tbz' in several locations. "
But unlike the two previous versions of MyDoom, this third variant does not spread via e-mail, nor does it install a backdoor on infected machines or have a kill date, according to an analysis done by Ken Dunham, malicious code manager for iDefense Inc., based in Reston, Va. The worm's code is not encrypted, but it contains all of the source code for MyDoom.A.
The new worm's infection procedure may limit its spread, experts said. MyDoom.C spreads by scanning for machines that are already infected with one of the other variants of the worm. So the possibility of spreading widely in the enterprise is mitigated by the fact that most companies affected by one of the other worms likely already has cleaned up those PCs. Also, administrators can trump the new variant by blocking Port 3127 at the firewall.
"The risk presented by Mydoom.C needs to be tempered with the fact it is easily foiled by protection available from as early as two weeks ago. The fact the worm preys on existing Mydoom infected computers is much like a flock of vultures circling around an unfortunate soul about to succumb to the elements in that it is picking through scraps," said Ian Hameroff, eTrust security strategist at Computer Associates International Inc. of Islandia, N.Y.…
MyDoom.C does have the ability to launch a denial-of-service attack against Microsoft's main Web site, which experienced some severe performance problems overnight Sunday and again Monday morning, according to data compiled by Netcraft Ltd. If the worm is started between Feb. 8 and Feb. 12, it starts a thread that sleeps for a random amount of time and then spawns 80 threads that begin requesting pages from Microsoft.com at once. MyDoom.C does not try to attack The SCO Group's Web site, however, as the two previous versions did.…
http://www.eweek.com/article2/0,4149,1522236,00.asp
"UPDATED: A stripped-down version of the MyDoom worm, a k a Doomjuice, on Monday spread through network backdoor and attacked Microsoft's Web site.
A new version of the MyDoom worm appears to be circulating on the Internet and may be responsible for some disruptions to Microsoft Corp.'s Web site Sunday night and Monday morning, researchers said.
When it's executed, the new variant, called MyDoom.C, or Doomjuice, begins scanning for machines listening on TCP port 3127. When it finds available PCs, it copies itself to the new machine's Windows directory under the file name 'intrenat.exe' and also creates a file named 'sync-src-1.00.tbz' in several locations. "
But unlike the two previous versions of MyDoom, this third variant does not spread via e-mail, nor does it install a backdoor on infected machines or have a kill date, according to an analysis done by Ken Dunham, malicious code manager for iDefense Inc., based in Reston, Va. The worm's code is not encrypted, but it contains all of the source code for MyDoom.A.
The new worm's infection procedure may limit its spread, experts said. MyDoom.C spreads by scanning for machines that are already infected with one of the other variants of the worm. So the possibility of spreading widely in the enterprise is mitigated by the fact that most companies affected by one of the other worms likely already has cleaned up those PCs. Also, administrators can trump the new variant by blocking Port 3127 at the firewall.
"The risk presented by Mydoom.C needs to be tempered with the fact it is easily foiled by protection available from as early as two weeks ago. The fact the worm preys on existing Mydoom infected computers is much like a flock of vultures circling around an unfortunate soul about to succumb to the elements in that it is picking through scraps," said Ian Hameroff, eTrust security strategist at Computer Associates International Inc. of Islandia, N.Y.…
MyDoom.C does have the ability to launch a denial-of-service attack against Microsoft's main Web site, which experienced some severe performance problems overnight Sunday and again Monday morning, according to data compiled by Netcraft Ltd. If the worm is started between Feb. 8 and Feb. 12, it starts a thread that sleeps for a random amount of time and then spawns 80 threads that begin requesting pages from Microsoft.com at once. MyDoom.C does not try to attack The SCO Group's Web site, however, as the two previous versions did.…
http://www.eweek.com/article2/0,4149,1522236,00.asp
Tuesday, February 10, 2004
Chicago Tribune | 'Mydoom' Creators Start Up 'Doomjuice':
"Finnish computer security experts warned Tuesday of a new worm, known as 'Doomjuice,' that is expected to attack computers infected by 'Mydoom,' despite the fact it's programmed to stop spreading later this week.
The virus, first detected by F-Secure on Monday night, has so far infected at least 30,000 computers worldwide since it was activated Sunday, said the company's director of antivirus research, Mikko Hypponen. "
Like Mydoom.A and Mydoom.B, the new worm is designed to strike Microsoft Corp.'s Windows operating systems and is programmed to launch a worldwide attack on the web site of SCO, one of the largest UNIX vendors in the world.
"Unlike Mydoom, it does not spread via e-mail. It comes through a backdoor left open by Mydoom," Hypponen told The Associated Press. "People won't even realize their computers are being attacked, and then they'll have both Mydoom and Doomjuice in their computers."
Doomjuice drops the original source code of the Mydoom.A worm in an archive to folders on infected computers.
"This proves to us that Doomjuice and Mydoom.A are written by the same people," Hypponen said. "The source code of Mydoom.A has not been seen circulating in the underground before."
Doomjuice's ability to spread is limited because it will only attack computers infected by Mydoom, Hypponen said. "And lots of them are being cleaned up already at a quick rate."
But, he warned, unlike Mydoom which is programmed to stop spreading on Feb. 12, Doomjuice could run forever. "At least until all computers everywhere infected by both worms have been cleaned up, and that could be years," Hypponen said.
F-Secure said it is difficult to fully assess how destructive Doomjuice has been so far, but that one sensor monitoring a fifth of the world's Internet traffic Monday found 30,000 hits.
So far, www.microsoft.com, one of the largest web sites in the world, appears to be operational, but F-Secure had noticed a disruption in service on Monday.
F-Secure: http://F-Secure.com/
http://www.chicagotribune.com/technology/sns-ap-finland-doomjuice-worm.story
"Finnish computer security experts warned Tuesday of a new worm, known as 'Doomjuice,' that is expected to attack computers infected by 'Mydoom,' despite the fact it's programmed to stop spreading later this week.
The virus, first detected by F-Secure on Monday night, has so far infected at least 30,000 computers worldwide since it was activated Sunday, said the company's director of antivirus research, Mikko Hypponen. "
Like Mydoom.A and Mydoom.B, the new worm is designed to strike Microsoft Corp.'s Windows operating systems and is programmed to launch a worldwide attack on the web site of SCO, one of the largest UNIX vendors in the world.
"Unlike Mydoom, it does not spread via e-mail. It comes through a backdoor left open by Mydoom," Hypponen told The Associated Press. "People won't even realize their computers are being attacked, and then they'll have both Mydoom and Doomjuice in their computers."
Doomjuice drops the original source code of the Mydoom.A worm in an archive to folders on infected computers.
"This proves to us that Doomjuice and Mydoom.A are written by the same people," Hypponen said. "The source code of Mydoom.A has not been seen circulating in the underground before."
Doomjuice's ability to spread is limited because it will only attack computers infected by Mydoom, Hypponen said. "And lots of them are being cleaned up already at a quick rate."
But, he warned, unlike Mydoom which is programmed to stop spreading on Feb. 12, Doomjuice could run forever. "At least until all computers everywhere infected by both worms have been cleaned up, and that could be years," Hypponen said.
F-Secure said it is difficult to fully assess how destructive Doomjuice has been so far, but that one sensor monitoring a fifth of the world's Internet traffic Monday found 30,000 hits.
So far, www.microsoft.com, one of the largest web sites in the world, appears to be operational, but F-Secure had noticed a disruption in service on Monday.
F-Secure: http://F-Secure.com/
http://www.chicagotribune.com/technology/sns-ap-finland-doomjuice-worm.story
Monday, February 09, 2004
MyDoom sparks talks of security's future - News - ZDNet:
"Despite a deep understanding of how such viruses spread, security experts seem to be at a loss at how to stop them. Popular antivirus technology is generally ineffectual against many of the attacks until an update is downloaded by the user. Moreover, even though antivirus software is the most popular security technology in use--about 99 percent of corporations use it, according to the Computer Security Institute--many home users still don't use the software.
'Many people don't even have the software,' said Bruce Schneier, chief technology officer for Counterpane Internet Security. 'And for those that do, the first few hours of an epidemic is a race against time.' "
MyDoom spread through e-mail a week ago, infecting a new computer every time an unwary user opened the attached filed containing the program. As many as 2 million computers may have been infected. The original virus was programmed to attack The SCO Group's Web site last Sunday, while a variant is scheduled to target Microsoft on Tuesday.
E-mail service provider MessageLabs has quarantined more than 17 million e-mail messages in a week, said Alex Shipp, senior antivirus technologist for the company. From data captured early in the epidemic, MessageLabs says that for every Internet address with an infected PC behind it, eight e-mails are sent, on average, to one of the company's customers.
However, even though companies are still seeing massive quantities of e-mail messages bearing the MyDoom virus, the spread has slowed, stressed Shipp.…
http://zdnet.com.com/2100-1105_2-5152165.html?tag=zdaresources
"Despite a deep understanding of how such viruses spread, security experts seem to be at a loss at how to stop them. Popular antivirus technology is generally ineffectual against many of the attacks until an update is downloaded by the user. Moreover, even though antivirus software is the most popular security technology in use--about 99 percent of corporations use it, according to the Computer Security Institute--many home users still don't use the software.
'Many people don't even have the software,' said Bruce Schneier, chief technology officer for Counterpane Internet Security. 'And for those that do, the first few hours of an epidemic is a race against time.' "
MyDoom spread through e-mail a week ago, infecting a new computer every time an unwary user opened the attached filed containing the program. As many as 2 million computers may have been infected. The original virus was programmed to attack The SCO Group's Web site last Sunday, while a variant is scheduled to target Microsoft on Tuesday.
E-mail service provider MessageLabs has quarantined more than 17 million e-mail messages in a week, said Alex Shipp, senior antivirus technologist for the company. From data captured early in the epidemic, MessageLabs says that for every Internet address with an infected PC behind it, eight e-mails are sent, on average, to one of the company's customers.
However, even though companies are still seeing massive quantities of e-mail messages bearing the MyDoom virus, the spread has slowed, stressed Shipp.…
http://zdnet.com.com/2100-1105_2-5152165.html?tag=zdaresources
Friday, February 06, 2004
IE security patch nixes some apps - News - ZDNet:
"Some Web developers are complaining that an Internet Explorer patch that's meant to foil Net scams is disabling some applications that didn't put a premium on security.
Microsoft last week announced that a modification to its IE browser would stop the insecure practice of including sensitive information in links. The update, which was released Monday, had some Web site programmers up in arms Wednesday due to complaints from Web users that they could no longer log in to sites that secure entry through credentials included in the URL.
'Microsoft may have legitimate reasons for addressing the issue, but the way they addressed it--an across-the-board kill of an industry standard--is troublesome,' said James Rosko, a software engineer for a data-processing service on the Web. He and other programmers spent Tuesday night making changes to the programs that process login requests for his company's Web site, which he requested not be named."
The incident could be the first known case of Microsoft getting attention for putting security before a feature used by some of its customers. Microsoft promised to put security first when it launched its Trustworthy Computing Initiative more than two years ago. But some critics have claimed that they haven't seen many results.…
The problem occurs when programmers design a Web site to enable a Web user to log in by typing credentials into the URL. In such cases, the Web address might look like this: http://username:password@www.somecompany.com/program.ext. The link gives the person access to a company's Web site when the authentication program verifies the username and password.
Because the username and password are part of the Web address and are not encrypted, embedding the credential in the URL is considered a security risk, said William Kennedy, chief technology officer at ActivMedia Robotics and the co-author of "HTML & XHTML: The Definitive Guide."
"It was a dumb idea to include such functionality in the first place," Kennedy said. "There are millions of other ways of logging in to a site."
However, that sentiment was not what made Microsoft disable the feature. The software giant made the change to stop scam artists from constructing URLs that appeared to link to a legitimate Web site but actually directed people to a fraudulent site. For instance, a URL that appears to go to eBay could actually send the person to a fraudulent site such as: http://www.ebay.com@fraudsite.com.
The fake site will typically ask for a person's username and password and then use that information to complete a scam. Major banks and other financial Web sites, such as PayPal, are popular targets of such fraud, often called "phishing." The Federal Deposit Insurance Corp., the government organization that underwrites U.S. citizens' banks accounts, recently warned of a similar scam.…
http://zdnet.com.com/2100-1105_2-5153534.html
"Some Web developers are complaining that an Internet Explorer patch that's meant to foil Net scams is disabling some applications that didn't put a premium on security.
Microsoft last week announced that a modification to its IE browser would stop the insecure practice of including sensitive information in links. The update, which was released Monday, had some Web site programmers up in arms Wednesday due to complaints from Web users that they could no longer log in to sites that secure entry through credentials included in the URL.
'Microsoft may have legitimate reasons for addressing the issue, but the way they addressed it--an across-the-board kill of an industry standard--is troublesome,' said James Rosko, a software engineer for a data-processing service on the Web. He and other programmers spent Tuesday night making changes to the programs that process login requests for his company's Web site, which he requested not be named."
The incident could be the first known case of Microsoft getting attention for putting security before a feature used by some of its customers. Microsoft promised to put security first when it launched its Trustworthy Computing Initiative more than two years ago. But some critics have claimed that they haven't seen many results.…
The problem occurs when programmers design a Web site to enable a Web user to log in by typing credentials into the URL. In such cases, the Web address might look like this: http://username:password@www.somecompany.com/program.ext. The link gives the person access to a company's Web site when the authentication program verifies the username and password.
Because the username and password are part of the Web address and are not encrypted, embedding the credential in the URL is considered a security risk, said William Kennedy, chief technology officer at ActivMedia Robotics and the co-author of "HTML & XHTML: The Definitive Guide."
"It was a dumb idea to include such functionality in the first place," Kennedy said. "There are millions of other ways of logging in to a site."
However, that sentiment was not what made Microsoft disable the feature. The software giant made the change to stop scam artists from constructing URLs that appeared to link to a legitimate Web site but actually directed people to a fraudulent site. For instance, a URL that appears to go to eBay could actually send the person to a fraudulent site such as: http://www.ebay.com@fraudsite.com.
The fake site will typically ask for a person's username and password and then use that information to complete a scam. Major banks and other financial Web sites, such as PayPal, are popular targets of such fraud, often called "phishing." The Federal Deposit Insurance Corp., the government organization that underwrites U.S. citizens' banks accounts, recently warned of a similar scam.…
http://zdnet.com.com/2100-1105_2-5153534.html
Geeks Put the Unsavvy on Alert: Learn or Log Off:
"The tension over the MyDoom virus underscores a growing friction between technophiles and what they see as a breed of technophobes who want to enjoy the benefits of digital technology without making the effort to use it responsibly.
The virus spreads when Internet users ignore a basic rule of Internet life: never click on an unknown e-mail attachment. Once someone does, MyDoom begins to send itself to the names in that person's e-mail address book. If no one opened the attachment, the virus's destructive power would never be unleashed."
"It takes affirmative action on the part of the clueless user to become infected," wrote Scott Bowling, president of the World Wide Web Artists Consortium, expressing frustration on the group's discussion forum. "How to beat this into these people's heads?"
Many of the million or so people who have so far infected their computers with MyDoom say it is not their fault. The virus often comes in a message that appears to be from someone they know, with an innocuous subject line like "test" or "error." It is human nature, they say, to open the mail and attachments.
But computer sophisticates say it reflects a willful ignorance of basic computer skills that goes well beyond virus etiquette. At a time when more than two-thirds of American adults use the Internet, they say, such carelessness is no longer excusable, particularly when it messes things up for everyone else.…
http://www.nytimes.com/2004/02/05/technology/05VIRU.html?pagewanted=all&position=
"The tension over the MyDoom virus underscores a growing friction between technophiles and what they see as a breed of technophobes who want to enjoy the benefits of digital technology without making the effort to use it responsibly.
The virus spreads when Internet users ignore a basic rule of Internet life: never click on an unknown e-mail attachment. Once someone does, MyDoom begins to send itself to the names in that person's e-mail address book. If no one opened the attachment, the virus's destructive power would never be unleashed."
"It takes affirmative action on the part of the clueless user to become infected," wrote Scott Bowling, president of the World Wide Web Artists Consortium, expressing frustration on the group's discussion forum. "How to beat this into these people's heads?"
Many of the million or so people who have so far infected their computers with MyDoom say it is not their fault. The virus often comes in a message that appears to be from someone they know, with an innocuous subject line like "test" or "error." It is human nature, they say, to open the mail and attachments.
But computer sophisticates say it reflects a willful ignorance of basic computer skills that goes well beyond virus etiquette. At a time when more than two-thirds of American adults use the Internet, they say, such carelessness is no longer excusable, particularly when it messes things up for everyone else.…
http://www.nytimes.com/2004/02/05/technology/05VIRU.html?pagewanted=all&position=
Thursday, February 05, 2004
Do Web search engines suppress controversy?:
"Do Web search engines suppress controversy? by Susan L. Gerhart
Web behavior depends upon three interlocking communities: (1) authors whose Web pages link to other pages; (2) search engines indexing and ranking those pages; and (3) information seekers whose queries and surfing reward authors and support search engines. Systematic suppression of controversial topics would indicate a flaw in the Web’s ideology of openness and informativeness. This paper explores search engines’ bias by asking: Is a specific well–known controversy revealed in a simple search? Experimental topics include: distance learning, Albert Einstein, St. John’s Wort, female astronauts, and Belize. The experiments suggest simple queries tend to overly present the "sunny side" of these topics, with minimal controversy. A more "Objective Web" is analyzed where: (a) Web page authors adopt research citation practices; (b) search engines balance organizational and analytic content; and, (c) searchers practice more wary multi–searching.…"
http://www.firstmonday.dk/issues/issue9_1/gerhart/
"Do Web search engines suppress controversy? by Susan L. Gerhart
Web behavior depends upon three interlocking communities: (1) authors whose Web pages link to other pages; (2) search engines indexing and ranking those pages; and (3) information seekers whose queries and surfing reward authors and support search engines. Systematic suppression of controversial topics would indicate a flaw in the Web’s ideology of openness and informativeness. This paper explores search engines’ bias by asking: Is a specific well–known controversy revealed in a simple search? Experimental topics include: distance learning, Albert Einstein, St. John’s Wort, female astronauts, and Belize. The experiments suggest simple queries tend to overly present the "sunny side" of these topics, with minimal controversy. A more "Objective Web" is analyzed where: (a) Web page authors adopt research citation practices; (b) search engines balance organizational and analytic content; and, (c) searchers practice more wary multi–searching.…"
http://www.firstmonday.dk/issues/issue9_1/gerhart/
Wednesday, February 04, 2004
Microsoft shrugs off MyDoom attack - News - ZDNet:
"Microsoft has created an alternate Web site for people whose PCs are infected with MyDoom.B and who want to get security information but cannot contact the main site because of a mechanism in the virus that blocks some 65 Web sites, including Microsoft's home page. The alternate site, which starts with 'information' rather than 'www,' lets people see the regular home page content."
http://information.microsoft.com/
http://zdnet.com.com/2100-1105_2-5152702.html
"Microsoft has created an alternate Web site for people whose PCs are infected with MyDoom.B and who want to get security information but cannot contact the main site because of a mechanism in the virus that blocks some 65 Web sites, including Microsoft's home page. The alternate site, which starts with 'information' rather than 'www,' lets people see the regular home page content."
http://information.microsoft.com/
http://zdnet.com.com/2100-1105_2-5152702.html
Halting MyDoom Is a Free Download Away:
"MyDoom.A has 'DoS-ed' SCO.com out of commission, forcing the company to establish thescogroup.com in order to maintain its presence on the Internet. Microsoft, thus far, has fared better as MyDoom.B has yet to cripple the software giant's considerable defenses.
But where are individual PC users supposed to turn for relief?… "
http://www.enterpriseitplanet.com/security/news/article.php/3307751
"MyDoom.A has 'DoS-ed' SCO.com out of commission, forcing the company to establish thescogroup.com in order to maintain its presence on the Internet. Microsoft, thus far, has fared better as MyDoom.B has yet to cripple the software giant's considerable defenses.
But where are individual PC users supposed to turn for relief?… "
http://www.enterpriseitplanet.com/security/news/article.php/3307751
Google Ultimate Interface - Fagan Finder
If you want all of Google's tools and options conveniently displayed on a single screen, try FaganFinder.…It even has handy links for typing non-English letters.
http://www.faganfinder.com/google.html
If you want all of Google's tools and options conveniently displayed on a single screen, try FaganFinder.…It even has handy links for typing non-English letters.
http://www.faganfinder.com/google.html
Hidden Google Tools:
"Even if you consider yourself a Google expert, these 'hidden' tools and resources let you push the search engine's capabilities to the max.… "
http://searchenginewatch.com/searchday/article.php/3304771
"Even if you consider yourself a Google expert, these 'hidden' tools and resources let you push the search engine's capabilities to the max.… "
http://searchenginewatch.com/searchday/article.php/3304771
Microsoft Patches Serious IE Flaw:
"Microsoft Corp. on Monday finally released a patch for a dangerous vulnerability that lets attackers trick Internet users into visiting malicious sites. The flaw has been public knowledge for some time, but Microsoft failed to include a fix for it with January's scheduled patch releases.…"
http://www.eweek.com/article2/0,4149,1485698,00.asp
"Microsoft Corp. on Monday finally released a patch for a dangerous vulnerability that lets attackers trick Internet users into visiting malicious sites. The flaw has been public knowledge for some time, but Microsoft failed to include a fix for it with January's scheduled patch releases.…"
http://www.eweek.com/article2/0,4149,1485698,00.asp
IT Losing Ground in Virus Battle:
"After years of success deploying more effective and smarter defenses, anti-virus researchers contacted last week in the wake of the MyDoom outbreak acknowledged for one of the first times that the battle may be getting away from them.
The MyDoom virus, which hit Jan. 26 and infected several-hundred-thousand machines, is the fastest-spreading virus in the history of the Internet, experts said. At its peak late last week, MyDoom had infected one in every 12 pieces of e-mail, according to MessageLabs Inc., a New York-based e-mail security company. MyDoom also is the latest in a line of recent viruses that, while not particularly innovative, have been maddeningly effective.…"
http://www.eweek.com/print_article/0,3048,a=117996,00.asp
"After years of success deploying more effective and smarter defenses, anti-virus researchers contacted last week in the wake of the MyDoom outbreak acknowledged for one of the first times that the battle may be getting away from them.
The MyDoom virus, which hit Jan. 26 and infected several-hundred-thousand machines, is the fastest-spreading virus in the history of the Internet, experts said. At its peak late last week, MyDoom had infected one in every 12 pieces of e-mail, according to MessageLabs Inc., a New York-based e-mail security company. MyDoom also is the latest in a line of recent viruses that, while not particularly innovative, have been maddeningly effective.…"
http://www.eweek.com/print_article/0,3048,a=117996,00.asp
Tuesday, February 03, 2004
Accessible Website Menu: Ultimate Drop Down Menu by Brothercake:
"Ultimate Drop Down Menu v4.0 [beta] by Brothercake
UDM is a lightweight and accessible javascript menu, which provides useable content to all browsers - including screenreaders, search-engines and text-only browsers. But accessibility shouldn't mean compromise, and so UDM has a sophisticated range of design and usability controls, many of which are unique to this script.… "
http://af.brothercake.com/dropdown/
"Ultimate Drop Down Menu v4.0 [beta] by Brothercake
UDM is a lightweight and accessible javascript menu, which provides useable content to all browsers - including screenreaders, search-engines and text-only browsers. But accessibility shouldn't mean compromise, and so UDM has a sophisticated range of design and usability controls, many of which are unique to this script.… "
http://af.brothercake.com/dropdown/
Saturday, January 31, 2004
Another IE Spoofing Hole Found — sigh!:
"Security researchers are warning of another spoofing vulnerability in Internet Explorer, this time one that allows an attacker to mask the true file extension of malicious downloads.
The file-extension spoof means that an attacker could lull a user into opening a malicious file from a Web site by making the file appear as a legitimate extension, such as a PDF or MPEG, researchers said on Wednesday.… "
Users can avoid the vulnerability by first saving a download to a folder, rather than directly opening it, when prompted by IE. Saving the file reveals its true file name.
A Microsoft Corp. spokeswoman said the company is investigating the file-name spoofing vulnerability but could not say whether a fix would be ready at the same time as a planned patch for another IE spoofing vulnerability.
The other vulnerability, disclosed in December, could allow attackers to fake URLs in the Web browser's address bar and convince users to disclose sensitive information.
Microsoft officials have said they have a patch ready to fix that vulnerability but are testing it for multiple versions of IE on various platforms and for various languages.…
http://www.eweek.com/article2/0,4149,1473145,00.asp
"Security researchers are warning of another spoofing vulnerability in Internet Explorer, this time one that allows an attacker to mask the true file extension of malicious downloads.
The file-extension spoof means that an attacker could lull a user into opening a malicious file from a Web site by making the file appear as a legitimate extension, such as a PDF or MPEG, researchers said on Wednesday.… "
Users can avoid the vulnerability by first saving a download to a folder, rather than directly opening it, when prompted by IE. Saving the file reveals its true file name.
A Microsoft Corp. spokeswoman said the company is investigating the file-name spoofing vulnerability but could not say whether a fix would be ready at the same time as a planned patch for another IE spoofing vulnerability.
The other vulnerability, disclosed in December, could allow attackers to fake URLs in the Web browser's address bar and convince users to disclose sensitive information.
Microsoft officials have said they have a patch ready to fix that vulnerability but are testing it for multiple versions of IE on various platforms and for various languages.…
http://www.eweek.com/article2/0,4149,1473145,00.asp
Friday, January 30, 2004
Antivirus feature creates a burden - News - ZDNet:
"A common antivirus feature that automatically replies to e-mails infected with a virus--to inform the senders that they are infected--is obsolete and should be disabled, because it creates almost as much trouble as the virus itself, according to security experts.
When an antivirus application detects malware in an e-mail, such as the recent MyDoom worm, it can automatically reply to senders of messages to inform them that they have been infected. However, virtually all modern e-mail viruses disguise the original senders' addresses by spoofing the 'to' field of the reply message with stolen, but valid, e-mail addresses. This means that users receive e-mails telling them that they are infected when they are not, resulting in significant quantities of unnecessary traffic. "
This additional traffic is a further burden on administrators, because it occurs when companies are trying to clean their systems from the virus attack. Jack Clark, technology consultant at McAfee, an antivirus division of Network Associates, estimates that "bounce-back" e-mails play a significant part in slowing down corporate networks and says the feature should be disabled immediately.…
http://zdnet.com.com/2100-1105_2-5148995.html
"A common antivirus feature that automatically replies to e-mails infected with a virus--to inform the senders that they are infected--is obsolete and should be disabled, because it creates almost as much trouble as the virus itself, according to security experts.
When an antivirus application detects malware in an e-mail, such as the recent MyDoom worm, it can automatically reply to senders of messages to inform them that they have been infected. However, virtually all modern e-mail viruses disguise the original senders' addresses by spoofing the 'to' field of the reply message with stolen, but valid, e-mail addresses. This means that users receive e-mails telling them that they are infected when they are not, resulting in significant quantities of unnecessary traffic. "
This additional traffic is a further burden on administrators, because it occurs when companies are trying to clean their systems from the virus attack. Jack Clark, technology consultant at McAfee, an antivirus division of Network Associates, estimates that "bounce-back" e-mails play a significant part in slowing down corporate networks and says the feature should be disabled immediately.…
http://zdnet.com.com/2100-1105_2-5148995.html
Wednesday, January 28, 2004
Breaking Virus News: MyDoom Hobbles Internet E-mail:
"Removing/Blocking MyDoom
The easiest way to remove MyDoom and Novarg is to update your antivirus program. As of 1/27, most antivirus vendors have added at least beta detection and deletion to their pattern definition updates. If you don't have an antivirus, we have confirmation that TrendMicro's freely available Housecall http://housecall.trendmicro.com, has been updated to detect the virus, but you'll have to manually remove the registry entries as outlined below. Panda Software also has a free removal utility (registry required) for MyDoom, http://www.pandasoftware.com/ virus_info/encyclopedia/
overview.aspx?idvirus=44140. McAfee's stinger http://vil.nai.com/vil/stinger/ has also been updated to detect and remove MyDoom. Note that you need to reboot after running Stinger to completely repair your system."
http://www.pcmag.com/print_article/0,3048,a=117496,00.asp
"Removing/Blocking MyDoom
The easiest way to remove MyDoom and Novarg is to update your antivirus program. As of 1/27, most antivirus vendors have added at least beta detection and deletion to their pattern definition updates. If you don't have an antivirus, we have confirmation that TrendMicro's freely available Housecall http://housecall.trendmicro.com, has been updated to detect the virus, but you'll have to manually remove the registry entries as outlined below. Panda Software also has a free removal utility (registry required) for MyDoom, http://www.pandasoftware.com/ virus_info/encyclopedia/
overview.aspx?idvirus=44140. McAfee's stinger http://vil.nai.com/vil/stinger/ has also been updated to detect and remove MyDoom. Note that you need to reboot after running Stinger to completely repair your system."
http://www.pcmag.com/print_article/0,3048,a=117496,00.asp
Chicago Tribune | Computer users worldwide fall victim to worm:
"A rapidly spreading worm has infected personal computers worldwide, clogging e-mail traffic at an unprecedented pace.
Known as MyDoom, the worm is sent as an attachment and is contained in about one of every 12 e-mails sent, according to one security firm. Other experts said the message accounts for one in nine sent globally."
That volume makes MyDoom the most prolific worm or virus ever, according to security firm MessageLabs, surpassing last year's SoBig virus. SoBig was detected on one out of every 17 e-mails.
The worm propagates through cleverly written e-mail, Internet security analysts say. When opened, the worm replicates itself on e-mail addresses it finds and is sent on to new potential victims.
The worm doesn't exploit any flaws in the Windows operating system, but once inside a computer it releases a virus that allows the attackers to gain access and use the computer to launch an attack.…
The worm and its variant strains all have the same target: software firm SCO Group, of Lindon, Utah.
Infected computers are set to swamp SCO's Web site beginning Sunday in what is known as a denial-of-service attack. A successful denial-of-service attack causes a Web site to become inaccessible, effectively shutting it down. The attack is scheduled to start Sunday and continue until Feb. 12.
SCO owns the Unix computer operating system and maintains that Linux, a popular free operating system, infringes on its copyright by incorporating Unix features. SCO has gone to court to assert its ownership rights, angering some computer hackers who see Linux as an alternative to Microsoft's Windows.…
This is a pretty darned sophisticated worm," said David Perry, global education director for Trend Micro, a computer security company. "It is very well socially engineered."
Social engineering is a way of saying the worm is adept at getting users to open e-mail and activate the program.
The worm was first noticed Monday on the computer networks of major corporations, Perry said. That means the person who created MyDoom knows that corporate users can have hundreds or thousands of e-mail addresses on their computers, while home users typically have far fewer.
"If a corporate desktop gets infected, it can send out 5,000 or 6,000 e-mails in a tenth of a second," Perry said. He said that hundreds of thousands of computers have since become infected, in part because of MyDoom's rapid reproduction.
Many people know not to open suspicious e-mail or to click on e-mail attachments from strangers. But MyDoom "spoofs" its recipients by sometimes using the return e-mail address of an individual known to the target.
And the e-mail's message can be deceptive.
The subject line in some e-mails reads "Mail Transaction Failed," and the message includes "Partial message is available" and an icon to click.
Perry said such e-mail is a lot more likely to be opened than a typical spam message.…
http://www.chicagotribune.com/technology/chi-0401280318jan28,1,1664606.story?coll=chi-newsnationworld-hed
"A rapidly spreading worm has infected personal computers worldwide, clogging e-mail traffic at an unprecedented pace.
Known as MyDoom, the worm is sent as an attachment and is contained in about one of every 12 e-mails sent, according to one security firm. Other experts said the message accounts for one in nine sent globally."
That volume makes MyDoom the most prolific worm or virus ever, according to security firm MessageLabs, surpassing last year's SoBig virus. SoBig was detected on one out of every 17 e-mails.
The worm propagates through cleverly written e-mail, Internet security analysts say. When opened, the worm replicates itself on e-mail addresses it finds and is sent on to new potential victims.
The worm doesn't exploit any flaws in the Windows operating system, but once inside a computer it releases a virus that allows the attackers to gain access and use the computer to launch an attack.…
The worm and its variant strains all have the same target: software firm SCO Group, of Lindon, Utah.
Infected computers are set to swamp SCO's Web site beginning Sunday in what is known as a denial-of-service attack. A successful denial-of-service attack causes a Web site to become inaccessible, effectively shutting it down. The attack is scheduled to start Sunday and continue until Feb. 12.
SCO owns the Unix computer operating system and maintains that Linux, a popular free operating system, infringes on its copyright by incorporating Unix features. SCO has gone to court to assert its ownership rights, angering some computer hackers who see Linux as an alternative to Microsoft's Windows.…
This is a pretty darned sophisticated worm," said David Perry, global education director for Trend Micro, a computer security company. "It is very well socially engineered."
Social engineering is a way of saying the worm is adept at getting users to open e-mail and activate the program.
The worm was first noticed Monday on the computer networks of major corporations, Perry said. That means the person who created MyDoom knows that corporate users can have hundreds or thousands of e-mail addresses on their computers, while home users typically have far fewer.
"If a corporate desktop gets infected, it can send out 5,000 or 6,000 e-mails in a tenth of a second," Perry said. He said that hundreds of thousands of computers have since become infected, in part because of MyDoom's rapid reproduction.
Many people know not to open suspicious e-mail or to click on e-mail attachments from strangers. But MyDoom "spoofs" its recipients by sometimes using the return e-mail address of an individual known to the target.
And the e-mail's message can be deceptive.
The subject line in some e-mails reads "Mail Transaction Failed," and the message includes "Partial message is available" and an icon to click.
Perry said such e-mail is a lot more likely to be opened than a typical spam message.…
http://www.chicagotribune.com/technology/chi-0401280318jan28,1,1664606.story?coll=chi-newsnationworld-hed
Tuesday, January 27, 2004
HANDWRITING FONTS TO LOAD:
"How about borrowing somebody else's handwriting (especially if yours isn't all that neat to begin with)?"
Download the font you like, unzip the .zip file, and copy the .ttf file to your Fonts folder in your Windows directory.
http://pro.wanadoo.fr/dephitro/telechf1.htm
"How about borrowing somebody else's handwriting (especially if yours isn't all that neat to begin with)?"
Download the font you like, unzip the .zip file, and copy the .ttf file to your Fonts folder in your Windows directory.
http://pro.wanadoo.fr/dephitro/telechf1.htm
Friday, January 23, 2004
Easily and Safely Installing a Motherboard:
"Without a motherboard, your CPU is a very expensive silicon and plastic keychain accessory. Without a motherboard, that Radeon 9700 graphics card makes a great doorstop. Without a motherboard, there is no PC.
Motherboards used to be a pain in the derriere to install. A typical motherboard had zillions of jumper settings for different CPU clocks, frontside bus speeds, floating point coprocessors and memory module sizes. That time passed long ago, as chronology of technology is measured. Today's motherboards are more complex than ever, in terms of features sets, but are easier to install and simpler to set up than ever before.… "
http://www.extremetech.com/print_article/0,3998,a=34474,00.asp
"Without a motherboard, your CPU is a very expensive silicon and plastic keychain accessory. Without a motherboard, that Radeon 9700 graphics card makes a great doorstop. Without a motherboard, there is no PC.
Motherboards used to be a pain in the derriere to install. A typical motherboard had zillions of jumper settings for different CPU clocks, frontside bus speeds, floating point coprocessors and memory module sizes. That time passed long ago, as chronology of technology is measured. Today's motherboards are more complex than ever, in terms of features sets, but are easier to install and simpler to set up than ever before.… "
http://www.extremetech.com/print_article/0,3998,a=34474,00.asp
Thursday, January 22, 2004
Easing of Internet Regulations Challenges Surveillance Efforts:
"In a series of unpublicized meetings and heated correspondence in recent weeks, officials from the Justice Department, the Federal Bureau of Investigation and the Drug Enforcement Administration have repeatedly complained about the commission's decision in 2002 to classify high-speed Internet cable services under a looser regulatory regime than the phone system.
The Justice Department recently tried to block the commission from appealing a decision by a federal appeals court two months ago that struck down major parts of its 2002 deregulatory order. Justice Department officials fear that the deregulatory order impedes its ability to enforce wiretapping orders. "
The department ultimately decided to permit the F.C.C. to appeal, but took the highly unusual step of withdrawing from the lawsuit, officials involved in the case said.
As a result of the commission's actions, said John G. Malcolm, a deputy assistant attorney general who has played a lead role for the Justice Department, some telecommunications carriers have taken the position in court proceedings that they do not need to make their networks available to federal agents for court-approved wiretapping.
"I am aware of instances in which law enforcement authorities have not been able to execute intercept orders because of this uncertainty," Mr. Malcolm said in an interview last Friday. He declined to provide further details.
The clash between the commission and officials from the Justice Department and other law enforcement agencies pits two cherished policies of the Bush administration against each other. On one side stand those who support deregulation of major industries and the nurturing of emerging technologies; on the other are those who favor more aggressive law enforcement after the Sept. 11 terrorist attacks.
The outcome of the debate has far- reaching consequences.…
David Fiske, the commission's chief spokesman, said that he could not respond to Mr. Malcolm's statement that the F.C.C.'s interpretation of the rules was making it more difficult to execute surveillance orders.
A senior official at the F.C.C. said the commission was not unsympathetic to the concerns of the law enforcement agencies. "We're an economic regulatory agency as well as a law enforcement agency and we have to look at the interests of everyone," the official said.
Some industry experts say that their biggest worry is that law enforcement demands may reshape the technical specifications of the new Internet voice services, an accusation that officials at the Justice Department and the F.B.I. deny.
"What's most scary for industry and perhaps some people at the F.C.C. is the notion that the architecture of the Internet will depend on the permission of the F.B.I.," said Stewart A. Baker, a former general counsel of the National Security Agency, which monitors foreign communications. Mr. Baker now represents a number of telecommunications companies as a partner at the law firm of Steptoe & Johnson.
But law enforcement officials say they are not seeking uniform technical standards but requirements that the new companies offering so-called "voice over Internet" services build into their systems easy ways for agents to tap into conversations between suspects.
In a strange-bedfellows twist, officials from the F.B.I. and other agencies have found themselves the unlikely allies of groups like the American Civil Liberties Union, which have also argued that the new Internet services offered by cable companies should be under a regulatory regime like the phone system — but for different reasons. The A.C.L.U. prefers that approach because it would prohibit cable companies from discriminating against Internet service providers, and as such would assure a greater diversity of voices.…
http://www.nytimes.com/2004/01/22/technology/22VOIC.html?pagewanted=all&position=
"In a series of unpublicized meetings and heated correspondence in recent weeks, officials from the Justice Department, the Federal Bureau of Investigation and the Drug Enforcement Administration have repeatedly complained about the commission's decision in 2002 to classify high-speed Internet cable services under a looser regulatory regime than the phone system.
The Justice Department recently tried to block the commission from appealing a decision by a federal appeals court two months ago that struck down major parts of its 2002 deregulatory order. Justice Department officials fear that the deregulatory order impedes its ability to enforce wiretapping orders. "
The department ultimately decided to permit the F.C.C. to appeal, but took the highly unusual step of withdrawing from the lawsuit, officials involved in the case said.
As a result of the commission's actions, said John G. Malcolm, a deputy assistant attorney general who has played a lead role for the Justice Department, some telecommunications carriers have taken the position in court proceedings that they do not need to make their networks available to federal agents for court-approved wiretapping.
"I am aware of instances in which law enforcement authorities have not been able to execute intercept orders because of this uncertainty," Mr. Malcolm said in an interview last Friday. He declined to provide further details.
The clash between the commission and officials from the Justice Department and other law enforcement agencies pits two cherished policies of the Bush administration against each other. On one side stand those who support deregulation of major industries and the nurturing of emerging technologies; on the other are those who favor more aggressive law enforcement after the Sept. 11 terrorist attacks.
The outcome of the debate has far- reaching consequences.…
David Fiske, the commission's chief spokesman, said that he could not respond to Mr. Malcolm's statement that the F.C.C.'s interpretation of the rules was making it more difficult to execute surveillance orders.
A senior official at the F.C.C. said the commission was not unsympathetic to the concerns of the law enforcement agencies. "We're an economic regulatory agency as well as a law enforcement agency and we have to look at the interests of everyone," the official said.
Some industry experts say that their biggest worry is that law enforcement demands may reshape the technical specifications of the new Internet voice services, an accusation that officials at the Justice Department and the F.B.I. deny.
"What's most scary for industry and perhaps some people at the F.C.C. is the notion that the architecture of the Internet will depend on the permission of the F.B.I.," said Stewart A. Baker, a former general counsel of the National Security Agency, which monitors foreign communications. Mr. Baker now represents a number of telecommunications companies as a partner at the law firm of Steptoe & Johnson.
But law enforcement officials say they are not seeking uniform technical standards but requirements that the new companies offering so-called "voice over Internet" services build into their systems easy ways for agents to tap into conversations between suspects.
In a strange-bedfellows twist, officials from the F.B.I. and other agencies have found themselves the unlikely allies of groups like the American Civil Liberties Union, which have also argued that the new Internet services offered by cable companies should be under a regulatory regime like the phone system — but for different reasons. The A.C.L.U. prefers that approach because it would prohibit cable companies from discriminating against Internet service providers, and as such would assure a greater diversity of voices.…
http://www.nytimes.com/2004/01/22/technology/22VOIC.html?pagewanted=all&position=
Wednesday, January 21, 2004
Report Says Internet Voting System Is Too Insecure to Use:
"A new $22 million system to allow soldiers and other Americans overseas to vote via the Internet is inherently insecure and should be abandoned, according to a panel of computer security experts asked by the government to review the program.
The system, Secure Electronic Registration and Voting Experiment, or SERVE, was developed with financing from the Department of Defense and will first be used in this year's primaries and general election."
The authors of the new report noted that computer security experts had already voiced increasingly strong warnings about the reliability of electronic voting systems, but they said the new voting program, which allows people overseas to vote from their personal computers over the Internet, raised the ante on such systems' risks.
The system, they wrote, "has numerous other fundamental security problems that leave it vulnerable to a variety of well-known cyber attacks, any one of which could be catastrophic." Any system for voting over the Internet with common personal computers, they noted, would suffer from the same risks.
The trojans, viruses and other attacks that complicate modern life and allow such crimes as online snooping and identity theft could enable hackers to disrupt or even alter the course of elections, the report concluded. Such attacks "could have a devastating effect on public confidence in elections," the report's authors wrote, and so "the best course to take is not to field the SERVE system at all." …
http://www.nytimes.com/2004/01/21/technology/23CND-INTE.html?pagewanted=all&position=
"A new $22 million system to allow soldiers and other Americans overseas to vote via the Internet is inherently insecure and should be abandoned, according to a panel of computer security experts asked by the government to review the program.
The system, Secure Electronic Registration and Voting Experiment, or SERVE, was developed with financing from the Department of Defense and will first be used in this year's primaries and general election."
The authors of the new report noted that computer security experts had already voiced increasingly strong warnings about the reliability of electronic voting systems, but they said the new voting program, which allows people overseas to vote from their personal computers over the Internet, raised the ante on such systems' risks.
The system, they wrote, "has numerous other fundamental security problems that leave it vulnerable to a variety of well-known cyber attacks, any one of which could be catastrophic." Any system for voting over the Internet with common personal computers, they noted, would suffer from the same risks.
The trojans, viruses and other attacks that complicate modern life and allow such crimes as online snooping and identity theft could enable hackers to disrupt or even alter the course of elections, the report concluded. Such attacks "could have a devastating effect on public confidence in elections," the report's authors wrote, and so "the best course to take is not to field the SERVE system at all." …
http://www.nytimes.com/2004/01/21/technology/23CND-INTE.html?pagewanted=all&position=
Saturday, January 17, 2004
Schneier.com: Crypto-Gram: January 15, 2004 — Color-Coded Terrorist Threat Levels:
"… the threat levels are largely motivated by politics. There are two possble reasons for the alert.
Reason 1: CYA. Governments are naturally risk averse, and issuing vague threat warnings makes sense from that perspective. Imagine if a terrorist attack actually did occur. If they didn't raise the threat level, they would be criticized for not anticipating the attack. As long as they raised the threat level they could always say 'We told you it was Orange,' even though the warning didn't come with any practical advice for people. "
Reason 2: To gain Republican votes. The Republicans spent decades running on the "Democrats are soft on Communism" platform. They've just discovered the "Democrats are soft on terrorism" platform. Voters who are constantly reminded to be fearful are more likely to vote Republican, or so the theory goes, because the Republicans are viewed as the party that is more likely to protect us.
(These reasons may sound cynical, but I believe that the Administration has not been acting in good faith regarding the terrorist threat, and their pronouncements in the press have to be viewed under that light.)
I can't think of any real security reasons for alerting the entire nation, and any putative terrorist plotters, that the Administration believes there is a credible threat.
http://www.schneier.com/crypto-gram-0401.html#1
"… the threat levels are largely motivated by politics. There are two possble reasons for the alert.
Reason 1: CYA. Governments are naturally risk averse, and issuing vague threat warnings makes sense from that perspective. Imagine if a terrorist attack actually did occur. If they didn't raise the threat level, they would be criticized for not anticipating the attack. As long as they raised the threat level they could always say 'We told you it was Orange,' even though the warning didn't come with any practical advice for people. "
Reason 2: To gain Republican votes. The Republicans spent decades running on the "Democrats are soft on Communism" platform. They've just discovered the "Democrats are soft on terrorism" platform. Voters who are constantly reminded to be fearful are more likely to vote Republican, or so the theory goes, because the Republicans are viewed as the party that is more likely to protect us.
(These reasons may sound cynical, but I believe that the Administration has not been acting in good faith regarding the terrorist threat, and their pronouncements in the press have to be viewed under that light.)
I can't think of any real security reasons for alerting the entire nation, and any putative terrorist plotters, that the Administration believes there is a credible threat.
http://www.schneier.com/crypto-gram-0401.html#1
Friday, January 16, 2004
News: Report: Spam claims two-thirds of e-mail:
"MessageLabs, an e-mail filtering company, claims 65 percent of e-mail sent to its users is spam, according to data it collected during December and released Monday.
While the statistics point to a dramatic upswing in the ratio of spam to legitimate e-mails--up from 43.7 percent in September, 50.5 percent in October and 55.1 percent in November--the figures only take into account e-mails being sent to MessageLabs' clients, many of whom signed up to the service because they received a high volume of spam, MessageLabs Australia's technical director David Banes conceded.… "
http://zdnet.com.com/2100-1105_2-5139469.html
"MessageLabs, an e-mail filtering company, claims 65 percent of e-mail sent to its users is spam, according to data it collected during December and released Monday.
While the statistics point to a dramatic upswing in the ratio of spam to legitimate e-mails--up from 43.7 percent in September, 50.5 percent in October and 55.1 percent in November--the figures only take into account e-mails being sent to MessageLabs' clients, many of whom signed up to the service because they received a high volume of spam, MessageLabs Australia's technical director David Banes conceded.… "
http://zdnet.com.com/2100-1105_2-5139469.html
Thursday, January 15, 2004
The Ten Immutable Laws of Security Administration :
"As in the case of the immutable laws for users, the laws on this list reflect the basic nature of security, rather than any product-specific issue. Don't look for a patch from a vendor, because these laws don't result from a technology flaw. Instead, use common sense and thorough planning to turn them to your advantage."
http://www.microsoft.com/technet/treeview/default.asp?url=/technet/columns/security/essays/10salaws.asp
"As in the case of the immutable laws for users, the laws on this list reflect the basic nature of security, rather than any product-specific issue. Don't look for a patch from a vendor, because these laws don't result from a technology flaw. Instead, use common sense and thorough planning to turn them to your advantage."
http://www.microsoft.com/technet/treeview/default.asp?url=/technet/columns/security/essays/10salaws.asp
Wednesday, January 14, 2004
News: Wi-Fi testing finds weak links:
"At least one in every four Wi-Fi products examined by the Wi-Fi Alliance has failed its certification test--a sign that many pieces of wireless equipment on the market are incapable of working as well as users might expect. "
Products that sport the Alliance's seal of approval are certified to work with each other and provide the performance expected from the 802.11a, b or g standards. This means that users can buy certified 802.11x routers, access points and cards knowing that they should all be compatible.
But while a great many Wi-Fi products have been approved by the Alliance, several hundred did not pass its tests.
"Based on testing of more than 1,000 products over several IEEE 802.11 standards, products that are prepared for Wi-Fi certification testing fail 25 (percent) to 30 percent of the time--or more depending on the technology being tested," said Wi-Fi Alliance managing director Frank Hanzlik.
"Products that do not go through the rigorous testing preparation process have an even higher failure rate. Without Wi-Fi certification, these product failures would have been experienced by the technology consumer," Hanzlik added.
A product that fails Wi-Fi certification can still be launched, though, and a manufacturer could still label its wireless products as "802.11b compatible" even if they only work with its own range of equipment and not with those from another company.
The Wi-Fi Alliance says that certification is becoming increasingly important as the wireless-networking market grows and matures.
http://zdnet.com.com/2100-1103_2-5139499.html
"At least one in every four Wi-Fi products examined by the Wi-Fi Alliance has failed its certification test--a sign that many pieces of wireless equipment on the market are incapable of working as well as users might expect. "
Products that sport the Alliance's seal of approval are certified to work with each other and provide the performance expected from the 802.11a, b or g standards. This means that users can buy certified 802.11x routers, access points and cards knowing that they should all be compatible.
But while a great many Wi-Fi products have been approved by the Alliance, several hundred did not pass its tests.
"Based on testing of more than 1,000 products over several IEEE 802.11 standards, products that are prepared for Wi-Fi certification testing fail 25 (percent) to 30 percent of the time--or more depending on the technology being tested," said Wi-Fi Alliance managing director Frank Hanzlik.
"Products that do not go through the rigorous testing preparation process have an even higher failure rate. Without Wi-Fi certification, these product failures would have been experienced by the technology consumer," Hanzlik added.
A product that fails Wi-Fi certification can still be launched, though, and a manufacturer could still label its wireless products as "802.11b compatible" even if they only work with its own range of equipment and not with those from another company.
The Wi-Fi Alliance says that certification is becoming increasingly important as the wireless-networking market grows and matures.
http://zdnet.com.com/2100-1103_2-5139499.html
Tuesday, January 13, 2004
Calendar Of Updates (Powered by Invision Power Board):
"Keep Your Security Software Current
Upgrades, Updates & Definitions"
… hard working people have put together a web site that deals with software updates, especially security updates. It is a free site where members can help with the updates.
Thanks to WinXPnews
http://www.winxpnews.com/issues.cfm
http://www.dozleng.com/updates/
"Keep Your Security Software Current
Upgrades, Updates & Definitions"
… hard working people have put together a web site that deals with software updates, especially security updates. It is a free site where members can help with the updates.
Thanks to WinXPnews
http://www.winxpnews.com/issues.cfm
http://www.dozleng.com/updates/
Monday, January 12, 2004
Microsoft Bows to Pressure, Extends Support for Older Windows Versions:
"Microsoft Corp. on Monday capitulated to customer pressure and announced that it would now continue extended support for Windows 98, Windows 98 Second Edition and for Windows Millennium Edition (ME) until June 30, 2006. "
… on Monday a company spokesman told eWEEK that the decision to extend support for the products was "part of Microsoft's ongoing effort to respond to customers' needs around the world." During this time, Microsoft will continue to offer paid phone support and will continue to review any critical security issues and take appropriate steps.
"Microsoft made this decision to accommodate customers worldwide who are still dependent upon these operating systems and to provide Microsoft more time to communicate its product lifecycle support guidelines in a handful of markets—particularly smaller and emerging markets," he said.
According to officials, Microsoft also wanted to bring Windows 98 SE into compliance with the company's current lifecycle policy for new products, which provides for support for seven years instead of the original four.
"Microsoft made the decision to also lengthen support for Windows 98 and Windows Me customers through the same date in order to provide a clear and consistent date for support conclusion for all of these older products," the spokesman said.
The move is expected to bring relief to some IT users, and particularly consumers, given the millions who still use the products.…
http://www.eweek.com/article2/0,4149,1434318,00.asp
"Microsoft Corp. on Monday capitulated to customer pressure and announced that it would now continue extended support for Windows 98, Windows 98 Second Edition and for Windows Millennium Edition (ME) until June 30, 2006. "
… on Monday a company spokesman told eWEEK that the decision to extend support for the products was "part of Microsoft's ongoing effort to respond to customers' needs around the world." During this time, Microsoft will continue to offer paid phone support and will continue to review any critical security issues and take appropriate steps.
"Microsoft made this decision to accommodate customers worldwide who are still dependent upon these operating systems and to provide Microsoft more time to communicate its product lifecycle support guidelines in a handful of markets—particularly smaller and emerging markets," he said.
According to officials, Microsoft also wanted to bring Windows 98 SE into compliance with the company's current lifecycle policy for new products, which provides for support for seven years instead of the original four.
"Microsoft made the decision to also lengthen support for Windows 98 and Windows Me customers through the same date in order to provide a clear and consistent date for support conclusion for all of these older products," the spokesman said.
The move is expected to bring relief to some IT users, and particularly consumers, given the millions who still use the products.…
http://www.eweek.com/article2/0,4149,1434318,00.asp
News: Windows 98 support shifts to CD:
"When Microsoft pulls the plug on Windows 98 support next Friday, it will offer a free CD designed to help users 'make the most' of the aging operating system, without any further assistance from the software giant.
Six years after its launch, Windows 98 is still used by about a fourth of Web surfers. Microsoft announced last year that it would stop supporting Windows 98 on Jan. 15, meaning that millions of users will soon be left exposed when new exploits and vulnerabilities are discovered. "
Lars Ahlgren, senior marketing manager at Microsoft, told ZDNet UK that the CD, which the software giant created with Future Publishing, will provide hints and tips, technical content and exclusive Knowledge Base articles. The content will also be published on Microsoft's support Web sites.
"We have made an arrangement with Future Publishing so we get Windows 98 content that is not just technical; it is also about how to get more from your Windows 98 machine. For those who have difficulties getting on the Web or want the content on a CD, we will ship them the CD for free, if they call us or register on the Web," Ahlgren said.
Ahlgren also acknowledged that Microsoft is hoping to keep Windows 98 users' expectations low, so that if there is a serious security breach the company decides to patch, they will be pleasantly surprised.…
http://zdnet.com.com/2100-1104_2-5138328.html
"When Microsoft pulls the plug on Windows 98 support next Friday, it will offer a free CD designed to help users 'make the most' of the aging operating system, without any further assistance from the software giant.
Six years after its launch, Windows 98 is still used by about a fourth of Web surfers. Microsoft announced last year that it would stop supporting Windows 98 on Jan. 15, meaning that millions of users will soon be left exposed when new exploits and vulnerabilities are discovered. "
Lars Ahlgren, senior marketing manager at Microsoft, told ZDNet UK that the CD, which the software giant created with Future Publishing, will provide hints and tips, technical content and exclusive Knowledge Base articles. The content will also be published on Microsoft's support Web sites.
"We have made an arrangement with Future Publishing so we get Windows 98 content that is not just technical; it is also about how to get more from your Windows 98 machine. For those who have difficulties getting on the Web or want the content on a CD, we will ship them the CD for free, if they call us or register on the Web," Ahlgren said.
Ahlgren also acknowledged that Microsoft is hoping to keep Windows 98 users' expectations low, so that if there is a serious security breach the company decides to patch, they will be pleasantly surprised.…
http://zdnet.com.com/2100-1104_2-5138328.html
Subscribe to:
Posts (Atom)

 Posts