Alias Reduces Educational Pricing on Alias SketchBook Pro: "
Alias, a Silicon Graphics Inc. company, announced special educational pricing for Alias SketchBook Pro, the sketching, annotation and presentation software for Tablet PCs and Wacom tablets. Following a restructuring of its education program in July 2003 to provide affordable and accessible Maya and StudioTools learning packages, Alias is now expanding the program to include reduced pricing on Alias SketchBook Pro for both students and faculty.
Alias SketchBook Pro provides the latest in accurate digital sketching technology for industries such as industrial and product design, architecture, computer graphics, animation, game development and fashion design. Students looking to break into these industries can benefit from combining tools like Alias SketchBook Pro and a Tablet PC or Wacom tablet to hone their skills and develop a portfolio of exceptional creative work.…"
www.alias.com
www.journeyed.com
http://www.emedialive.com/Newsletters/EMediaXtra.aspx?NewsletterID=140#4
Saturday, March 06, 2004


Paid Inclusion Under Fire at Search Engine Shindig:
"The debate over the fairness and relevancy of paid search spilled onto the stage at the Jupitermedia's Search Engine Strategies 2004 conference here on Wednesday.
On one side: Google Inc., which objects to any commingling of paid search with its Web index. On the other: Yahoo Inc., which embraced this week a program for letting Web sites pay to be included in its recently launched Web index. "
And in the middle: Ask Jeeves Inc., which has dropped one paid program, where Web sites could provide XML feeds into its index, while maintaining another for paying to submit sites for crawling.
The varying positions demonstrate the evolving field of Web search. The battle to deliver the most relevant results, and to make money, has intensified now that Yahoo has switched from Google's search results to its own technology and as Microsoft Corp. builds its own technology.
The latest shift was Ask Jeeves discontinuation of its Index Express program for direct XML feeds into its Teoma search engine index. Paul Gardi, Ask Jeeves senior vice president of operations and planning, said the company was not denouncing the practice of paid inclusion but dropped that form because it didn't return relevant results for users.…
Ask Jeeves, of Emeryville, Calif., is continuing its Site Submit program, where sites pay to guarantee that their pages get crawled, Gardi said.
But Google and Yahoo, in a far-reaching panel discussion here on the future of search, did stake out clear opinions on whether Web sites should be able to pay to ensure their pages are indexed.
Google will continue to ban any paid inclusion into its Web search index, said Craig Silverstein, Google's director of technology, which drew applause from the audience. The Mountain View, Calif., company follows a strict division between its advertising business for sponsored search links and its ranking of regular results, he said.…
http://www.eweek.com/article2/0,1759,1541921,00.asp
http://www.eweek.com/article2/0,1759,1542441,00.asp?kc=EWNWS030404DTX1K0000599
Wednesday, March 03, 2004
Microsoft Sparks Web Services for eBay:
"Specifically, developers may use Microsoft Office Excel 2003 spreadsheet and Microsoft Office FrontPage Web design applications to write services where eBay users could automate pricing and bid changes as needed. "
Participants in the eBay Developers Program can use XML application programming interfaces (APIs) with FrontPage 2003 to design Web sites that display custom information on items for sale on eBay. FrontPage 2003 includes Web design and maintenance tools and customized data views for listing multiple auction items.
With Excel 2003, users can: use XML to integrate with the eBay API to customize list views, graphs and charts; catalog bulk items online or offline; and submit item listings. The software allows eBay buyers and sellers to create a transaction record, analyze buying or selling history, and use automated uploading processes to submit listings.
To try the solution, users can download sample code with the eBay listing management capabilities within Microsoft Office from the eBay Developer site here.
http://developer.ebay.com/DevProgram/sign_in.asp?URL=/devzone/docs/samplecode.asp
http://www.internetnews.com/ec-news/article.php/3319641
Saturday, February 28, 2004
Netsky causing billions in damages - News - ZDNet:
"Despite requiring the computer user to actively run an attachment, Netsky.C seems to be spreading fast, with anti-virus vendor Central Command claiming it had discovered 1,500 infections of the virus within 40 minutes of its discovery. Like Netsky.B the latest virus uses its own SMTP engine to e-mail itself to addresses found on the computer, and copies itself into any folder it finds whose name includes 'shar'. "
UK security company mi2g estimated the economic damage done by Netsky.B worldwide to be at least US$3.12 billion. This was calculated "on the basis of helpdesk support costs, overtime payments, contingency outsourcing, loss of business, bandwidth clogging, productivity erosion, management time reallocation, cost of recovery, and software upgrades".…
http://zdnet.com.com/2100-1105_2-5165642.html
Thursday, February 26, 2004
Caller ID for E-Mail Technical Specification:
"'Caller ID for E-Mail: The Next Step to Deterring Spam' is the Microsoft draft specification to address the widespread problem of domain spoofing. Domain spoofing refers specifically to the use of someone else's domain name when sending a message, and is part of the larger spoofing problem, the practice of forging the sender's address on e-mail messages.
Caller ID for e-mail would verify that each e-mail message originates from the Internet domain it claims to come from. Eliminating domain spoofing will help legitimate senders protect their domain names and reputations, and help recipients more effectively identify and filter junk e-mail."
http://www.microsoft.com/mscorp/twc/privacy/spam_callerid.mspx
Fresh Worms Attack E-Mail, Internet Explorer, User Data:
"A series of new worms spread on the Internet on Wednesday, spreading through conventional e-mail methods. The new versions have escalated their attacks and destructiveness. "
On the prowl is MyDoom.F worm, which began action on Monday. It is the latest version one of most successful worms on record; earlier MyDoom variants in January launched a series of distributed denial of service attacks (DDoS) against Microsoft Corp. and The SCO Group. The new version retains its predecessors' capability to perform a DDoS attack.
"What is interesting about these latest worm trends is that they are very politically motivated. More than your curious teenage hacker at work; these attacks are stemming from groups seeking to make a statement on some of today's most controversial technology issues," said Scott Chasin, chief technology officer of MX Logic Inc., in a statement.
Beyond its DDoS target, MyDoom.F is also more destructive. A PC Magazine analysis of MyDoom.F, said the worm attempts to delete files on the system based on a probabilistic formula, adding an element of destructiveness rarely seen in such worms.
The worm also attempts to spread to file sharing users. For all these reasons, antivirus vendors are giving it a higher threat ranking than usual.
The latest threat is NetSky.C, which arrived on Wednesday. The worm is a variant of NetSky.B, which spread rapidly earlier this month, according to security vendors. It is also called Moodown.C.
According to F-Secure Corp.'s analysis of the worm, the new version is compressed with a different program. It also behaves differently in several ways than its predecessor, such as searching far more files for e-mail addresses that it can use to spread itself.
The worm arrives in a ZIP file attachment to an e-mail message. The file inside the ZIP will have two file extensions, the first for an innocuous file type such as .RTF and the second for an executable file type, such as .SCR.…
http://www.eweek.com/article2/0,4149,1538954,00.asp?kc=EWNWS022604DTX1K0000599
Security Guru Unmoved by Gates' RSA Remarks:
"Schneier's Gates comments followed some anecdotes about how everyone can help solve the security problems facing all enterprises. 'Get involved,' he said. 'That's how we make changes. Otherwise security is something done to us.'
Most security systems affect multiple parties, he explained, but usually only one person makes the decision about how security is implemented. 'At this point it's a negotiation. The players with most power are the ones who get to decide what the final answer is,' Schneier said. 'The best way to effect security is to gain power in negotiations. The best way is to change the environment in which security decisions are being made. Change the agenda of the players. Change the outcome.'
Every person has to make security work for himself, he said. 'The goal of security systems is the most security for the least amount of trade-offs. The way to do that is to make the party who is best able to mitigate the risk responsible for the risk,' he said, saying that computer software companies at this point do not share in the risks of software security or insecurity. "
Schneier said one of the best and simplest "security systems" he's seen is the local convenience store or fast food restaurant that displays a sign at the cash register that says, "Purchase free if you don't get a receipt." The system is not designed as a customer service, as it may appear, he said. Rather, it's a means of co-opting the customer into keeping an eye on the store employee who may be suspected of skimming from the cash register. Nevertheless, the customer will be watching if he knows he could get something for free.
"Good security systems are in line with their capabilities," he said. "The store manager is hiring you, aligning your interests with your capabilities. Very cheap security system. For the money it's really good. That's what we should strive for in security systems. The goal is to make them as effective as possible and work with the natural tendencies of people already there."
http://www.eweek.com/print_article/0,3048,a=120200,00.asp
News: Special Reports:
"RSA Conference: New lines of defense
The security companies and experts gathering at the RSA Conference 2004 in San Francisco are showing off smarter ways to ward off attacks. The problem is that hackers are becoming more sophisticated, too. At best, it's hoped that damage can be kept to a minimum."
http://zdnet.com.com/2251-1110-5163906.html
Wednesday, February 25, 2004
Service-Oriented Architecture: Chapter 13: Thirty best practices for integrating Web services. Pt. 1. - WebReference.com -:
"Service-Oriented Architecture: Chapter 13: Thirty best practices for integrating Web services, Pt. 1.
'This chapter is from the book 'Service-Oriented Architecture: A Field Guide to Integrating XML and Web Services' by Thomas Erl. (ISBN 0131428985)."
http://www.webreference.com/programming/soa/index.html
Tuesday, February 24, 2004
Download details: Office 2003/XP Add-in: Remove Hidden Data:
"With this add-in you can permanently remove hidden data and collaboration data, such as change tracking and comments, from Microsoft Word, Microsoft Excel, and Microsoft PowerPoint files."
Thanks to WinXPnews at http://www.winxpnews.com
http://www.microsoft.com/downloads/details.aspx?FamilyID=144e54ed-d43e-42ca-bc7b-5446d34e5360&displaylang=en
Monday, February 23, 2004
Order the Windows Security Update CD:
"Order the Windows Security Update CD
Updated Date: February 23, 2004
The Windows Security Update CD will be shipped to you free of charge. This CD includes Microsoft critical updates released through October 2003 and information to help you protect your PC. In addition, you will also receive a free antivirus and firewall trial software CD.
This CD is only available for Windows XP, Windows Me, Windows 2000, Windows 98, and Windows 98 Second Edition (SE).
Please allow 2-4 weeks for delivery."
http://www.microsoft.com/security/protect/cd/order.asp
Friday, February 20, 2004
Serious Linux Security Holes Uncovered and Patched:
"The Polish security non-profit organization iSEC Security Research on Wednesday released an advisory describing two 'critical security vulnerabilities' in Linux 2.4 and 2.6's 'kernel-memory-management code inside the 'mremap(2)' system call.… "
http://www.eweek.com/article2/0,4149,1530875,00.asp
"The Polish security non-profit organization iSEC Security Research on Wednesday released an advisory describing two 'critical security vulnerabilities' in Linux 2.4 and 2.6's 'kernel-memory-management code inside the 'mremap(2)' system call.… "
http://www.eweek.com/article2/0,4149,1530875,00.asp
Protect Your PC:
"* Exclusive offer for Microsoft customers. Free 12-month software subscription to CA's eTrust EZ Armor-LE Antivirus and Firewall security suite. Valid for new users only. Limit 1 per household. Not to be combined with any other offer. Customers may elect to upgrade to eTrust EZ Armor with enhanced firewall functionality. Annual subscriptions can be renewed after first year at current renewal rate. Free software offer expires 2/1/05. **IDC 2003. "
eTrust EZ Armor Security Suite from Computer Associates, the world's #1 supplier of Internet security software** combines award-winning Antivirus with industrial-strength Firewall protection. Built specifically for today's Internet-intensive computer user, eTrust EZ Armor leverages the core technology CA has developed for the world's most demanding users including over 99% of the Fortune 500.
EZ to install and a snap to use, eTrust EZ Armor provides automatic virus updates, advanced email attachment protection, EZ to use firewall settings, activity control to stop website monitoring, ad blocking and cookie control features for a more enjoyable Internet experience.
http://www.my-etrust.com/microsoft/
ZoneAlarm Bug Bares System to E-Mail Attack:
"Security vendor Zone Labs has disclosed that several versions of its personal-firewall products are vulnerable to a buffer-overflow attack that could compromise the system.
ZoneAlarm, ZoneAlarm Plus and ZoneAlarm Pro 4.0.0 versions; ZoneAlarm Pro 4.5.0; as well as Zone Labs Integrity Client 4.0.0 are vulnerable, the company said. Versions earlier than 4.0.0 are not. ZoneAlarm users are advised to upgrade to Version 4.5.538.001. (See the Zone Labs advisory for more details and how to obtain the upgrades.…"
http://download.zonelabs.com/bin/free/securityAlert/8.html
http://www.eweek.com/article2/0,4149,1531324,00.asp?kc=EWNWS022004DTX1K0000599
NetSky.B Worm Gains More Traction:
"A new mass-mailing worm, called NetSky.B, is spreading rapidly after beginning to make the rounds of e-mail inboxes on Tuesday.
NetSky.B is a variant of the NetSky.A worm identified earlier in the week, but is posing a greater risk of spreading and infecting machines, security vendors warned Wednesday. Symantec Corp. rated NetSky.B a Category 4 threat, its second-highest level, while Network Associates Inc. and F-Secure Corp. rated it as a medium threat.… "
Network Associates in its security alert (http://www.eweek.com/article2/0,4149,1530599,00.asp?kc=EWNWS022004DTX1K0000599) reports that NetSky.B attempts to deactivate the MyDoom.A and MyDoom.B viruses, which earlier this month overloaded e-mail inboxes worldwide and included payloads to trigger DoS (denial-of-service) attacks against the Web sites of the SCO Group Inc. and Microsoft Corp.
NetSky.B affects systems running Microsoft Windows 95 and higher.…
http://www.eweek.com/article2/0,4149,1530599,00.asp?kc=EWNWS022004DTX1K0000599
Wednesday, February 18, 2004
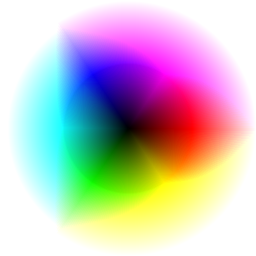
4096 Color Wheel:
"Hover over the wheel to view colors.
Click to choose a web-smart color.
Reload to clear."
Once, long ago, monitors could display only a restricted number of colors without dithering or other color discrepancies. The traditional solution to this problem was to use a restricted color palette known as the Netscape 216 colors, browser-safe colors or the web-safe colors. In hexadecimal form, the web-safe colors are composed of three pairs of identical hexadecimal digits selected from 00, 33, 66, 99, cc, and ff; for example, #000000 is black, and #ffffff is white.
Time passed, as it so frequently does, and new hardware supported thousands or millions of colors. People grew tired of the old 216 colors. They wanted more earth tones, more variety. The web-smart colors are those 4096 colors composed of any three pairs of identical hexadeximal digits (0-9 and a-f), such as #dd1188.
The unsafe colors are the full set of 16,777,216 hexadecimal colors, featuring any color between #000000 and #ffffff, such as #5a832d.
The current location of the 4096 Color Wheel is http://jemimap.ficml.org/style/color/wheel.html. The current version is 1.4. The Color Wheel is free for any use. To save it, download the html page and the image.
http://www.ficml.org/jemimap/style/color/colorwheel.png
http://www.ficml.org/jemimap/style/color/wheel.html
Security Alert: Bagle.B Worm Growing Fast:
"While the last Bagle virus scare turned out to be more hole than actual 'bagel,' this new variant is showing some real substance and is spreading at a rate that has some virus watchers upping Bagle.B-mm's threat level.
W32/Bagle.B-mm, also known as W32/Tanx.A, and Beagle.B, is a mass mailing worm that is spreading at outbreak proportions. Discovered, early Tuesday morning, MessageLabs has recorded over 75,000 copies of the virus detected from their customer base by 5 pm, with a peak infection ratio of 1 virus in 16 emails. The virus was classified as a medium threat by most antivirus vendors. Like its predecessor, Bagle.A, it is more performance degrading than destructive, though it sets up a Trojan to listen at a backdoor port, and uses its own SMTP engine to send copies to email addresses it finds on a victims system.
Bagle.B infected e-mails arrive with spoofed 'From' addresses, often people you know.…"
The virus normally runs the Windows sound recorder (sndrec32.exe) when it executes, though according to an analysis by Norman (http://www.norman.com/virus_info/w32_bagle_b_mm.shtml) Antivirus, "this will not happen if the worm starts as result of an update process or if it is started from the System directory." Sound recorder is just an indicator of infection, and put in to confuse the victim, and is not used further ( figure 2 ). However, the virus does open and listen at port 8866 to receive downloads or commands from the virus author. According to Symantec's analysis (http://www.sarc.com/avcenter/venc/data/w32.beagle.b@mm.html) of Bagle.B, the virus "Sends HTTP GET requests every 10,000 seconds to the following Web sites on TCP port 80:
www.strato.de/1.php
www.strato.de/2.php
www.47df.de/wbboard/1.php
www.intern.games-ring.de/2.php
Symantec also notes: "The GET request includes the port number that the infected computer is listening on, and the ID number that is saved in the 'gid' key in the Windows registry. Also, by connecting to the web server, the IP address will be sent." To propagate, Bagle.B harvests e-mail addresses from text based files and the Windows address book on the victim's PC. The virus creates e-mail messages with copies of itself as randomly named attachments, and sends using its own SMTP engine. Bagle.B will not send to email addresses containing the following:
.r1u
@hotmail.com
@msn.com
@microsoft
@avp
http://www.pcmag.com/print_article/0,3048,a=119435,00.asp
VoIP: It's not so easy to listen in - News - ZDNet:
"Jeff Pulver, founder of Free World Dialup, said Friday that if law enforcement officials asked him to wiretap one of his subscribers' Internet phone calls he would need a 'few months science project' to see if it could be done.
Meanwhile, Niklas Zennstrom, founder of Skype, also a free Internet phone service, said that even if his company could tackle the arduous task of pulling a Skype call from the Internet, police would 'only hear gibberish' because the data bits are encrypted."
The two providers are prime examples of a problem the Federal Communications Commission now faces after voting Thursday to investigate whether Internet phone providers should rewire their networks to government specifications to provide police with guaranteed access for wiretaps.
While many voice over Internet Protocol (VoIP) providers are more than willing to hand over whatever information they can about subscribers, they can't reliably, if at all, get what police really want: the content of the calls they make. Difficulties lie in gathering the millions of bits of information that represent a voice call as well as the fact that there is no standardized way for distinguishing voice calls from the terabits of other data on the Internet.
The issue affects a broad range of VoIP providers, including FWD and Skype, and commercial services such as Vonage and 8x8 that offer calls to traditional phone lines. Many of these commercial services say a sizable percentage of their calls never touch the traditional phone network and, as a result, cannot be tapped.…
http://zdnet.com.com/2100-1103_2-5159159.html
Tuesday, February 17, 2004
Download details: Mydoom (A, B) and Doomjuice (A, B) Worm Removal Tool (KB836528):
"This tool will help to remove the Mydoom.A, Mydoom.B, Doomjuice.A (aka "MyDoom.C"), and Doomjuice.B worms from infected systems. Once the tool has run—after the End-User License Agreement (EULA) is accepted—it automatically checks for infection and removes any of the targeted worms that are found. If a machine is infected with the Mydoom.B worm, the tool will also provide the user with the default version of the hosts file and set the "read-only" attribute for that file. This action will allow the user to visit previously-blocked Microsoft and antivirus websites."
After running, the tool displays a message describing the outcome of the detection and removal process. The tool can be safely deleted after it has run. Also, the tool creates a log file named doomcln.log in the %WINDIR%\debug folder.
This tool will not:
Detect or remove any viruses or worms other than Mydoom.A, Mydoom.B, Doomjuice.A, and Doomjuice.B
Detect or remove future variants of Mydoom or Doomjuice
Prevent the machine from being re-infected with Mydoom if, for example, an infected e-mail attachment is re-executed
Detect or remove malware that exists on a system as a result of the backdoor component created by Mydoom.A or Mydoom.B (besides Doomjuice.A and Doomjuice.B).
Delete any e-mail that contains Mydoom.A or Mydoom.B
Run on any version of Windows NT 4.0
The user must be an administrator to run this tool.…
http://www.microsoft.com/downloads/details.aspx?FamilyID=c14bfbe4-3d50-464d-a26c-9c287f8a08c5&displaylang=en
Chicago Tribune | Spammers Exploit High-Speed Connections:
"Next time you're looking for a culprit for all that junk mail flooding your inbox, have a glance in the mirror. Spammers are increasingly exploiting home computers with high-speed Internet connections into which they've cleverly burrowed.
E-mail security companies estimate that between one-third and two-thirds of unwanted messages are relayed unwittingly by PC owners who set up software incorrectly or fail to secure their machines.… "
Hundreds of thousands of computers worldwide have been infected by SoBig and other viruses that are programmed to spawn gateways, known technically as proxies, to relay spam. Though Lawrence had antivirus software, he hadn't kept it updated.
It's ironic to the president of the security Web site myNetWatchman.com, Lawrence Baldwin, that those afflicted by spam are also often its couriers.…
Any Internet-connected computer could be running a proxy spam relay, but most of the malicious programs are written specifically for PCs that run Windows.
In the past, some spammers had sought out and exploited Internet-connected computers with misconfigured networking software. The latest and growing threat is code purposely written to create spam relay proxies as it is spread by malicious viruses.
"It's just going to get worse," said Ken Schneider, chief technology officer at spam-filtering company Brightmail Inc. "Traditionally, virus writers were driven more by reputation and trying to impress each other. Now there's an economic motive."
Just last week, a proxy program called Mitglieder began installing itself on computers infected by last month's Mydoom outbreak, said Mikko Hypponen, manager of antivirus research at F-Secure Corp. in Finland. He said such programs can also sneak in if computer owners fail to install patches to fix known Windows flaws.
The shift in spamming methods even prompted the Federal Trade Commission to issue a consumer alert last month. The advisory encouraged consumers to use antivirus and firewall programs and to check "sent mail" folders for suspicious messages.
Others say home users should also keep their Windows operating systems up to date by visiting http://windowsupdate.microsoft.com.
"If your computer has been taken over by a spammer, you could face serious problems," the FTC advisory wrote. "Your Internet Service Provider (ISP) may prevent you from sending any e-mail at all until the virus is treated, and treatment could be a complicated, time-consuming process.…"
http://www.chicagotribune.com/technology/sns-ap-spam-zombies,1,2703344.story?coll=chi-technology-hed
Subscribe to:
Posts (Atom)

 Posts